On your ownReactive
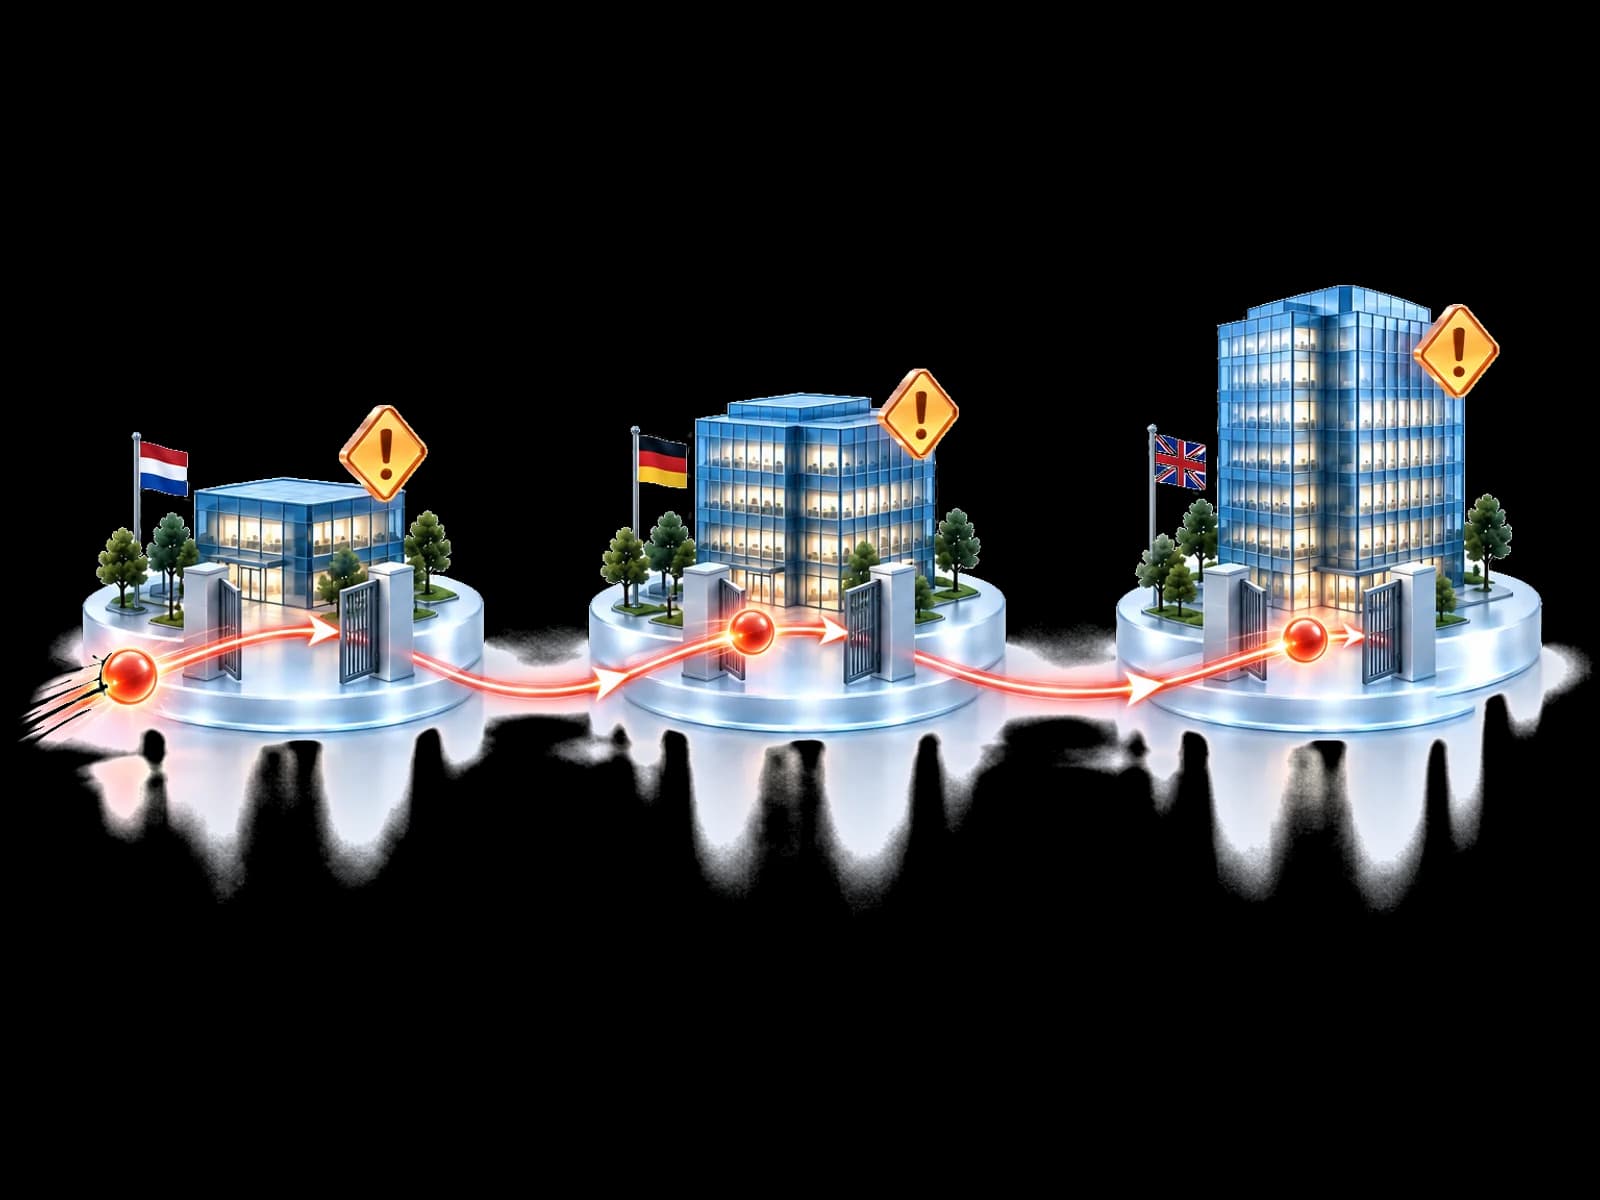
The same threat gets in again.
Known bad domains and sign-in patterns reach your people before anyone has checked them.
Front Gate Protection
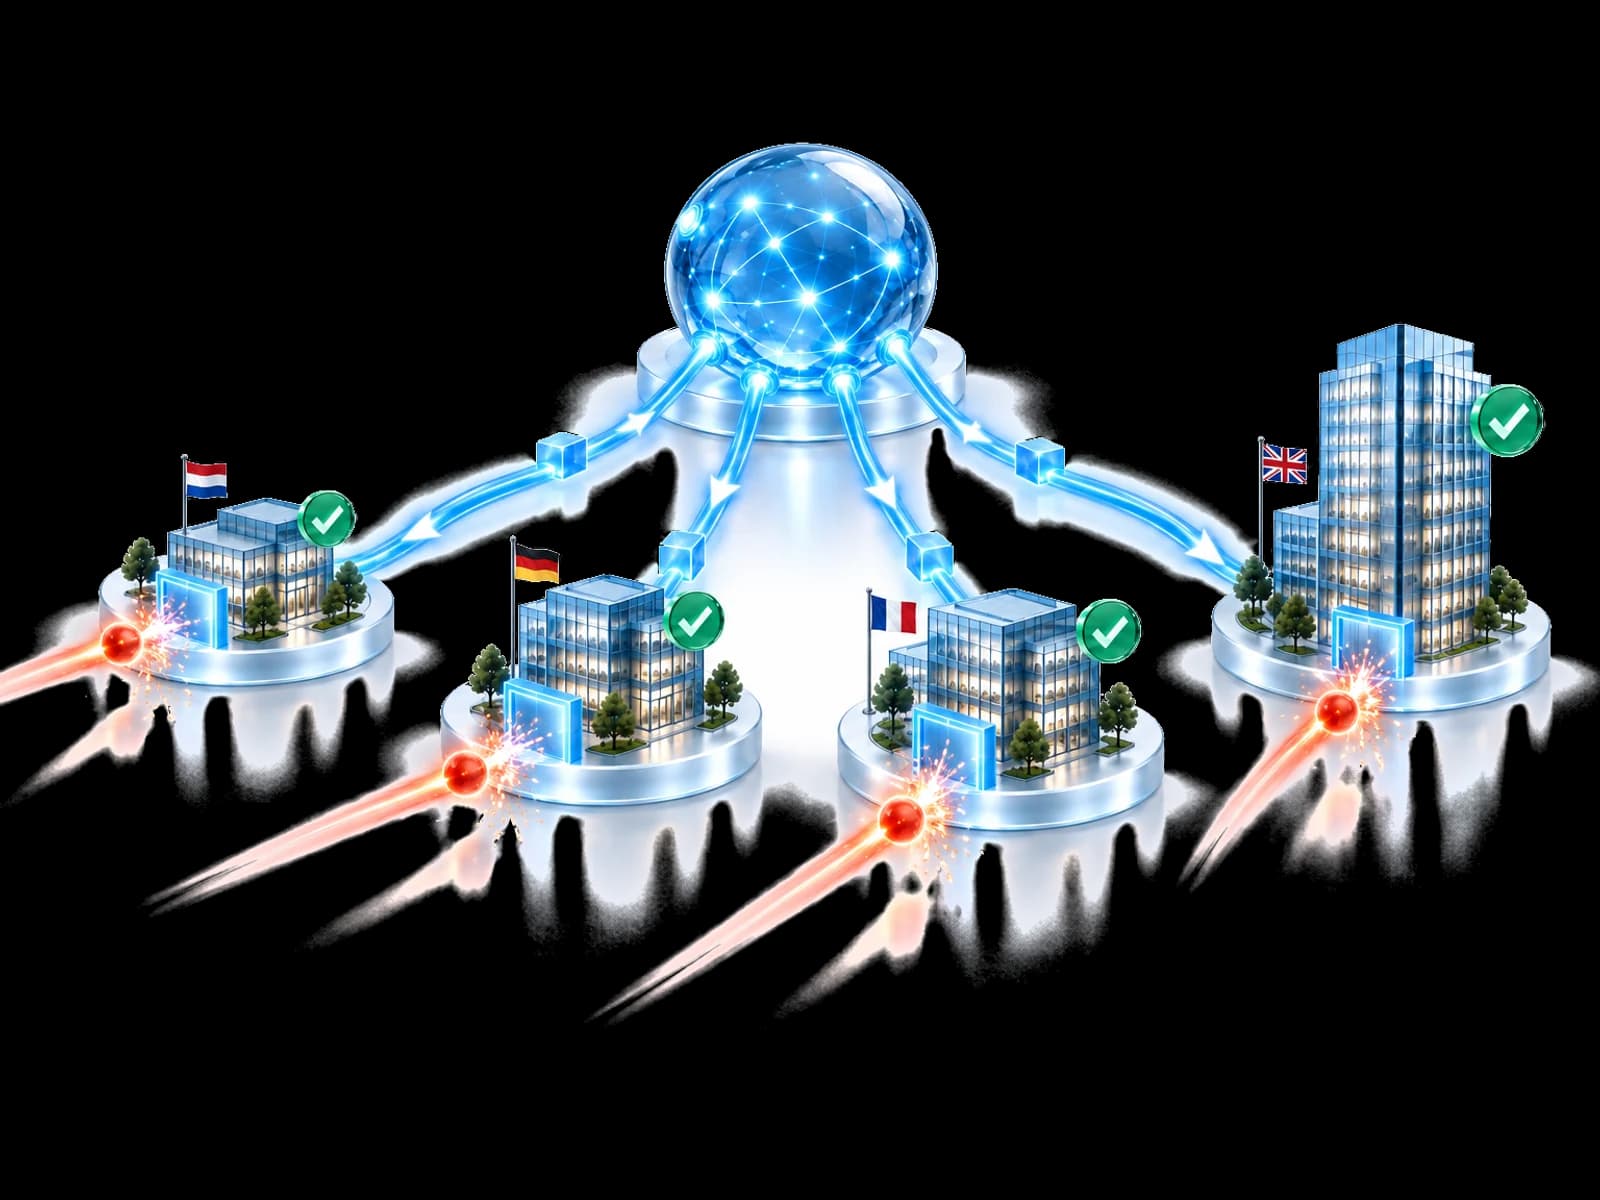
When a threat is confirmed elsewhere, UnifiedONE can turn it into protection at your front gate: supported Microsoft sign-in, email and device controls in your tenant, under your own policy.
Known threats can be blocked early. Your policy decides.Create your account and start your guided onboarding.
The problem
A threat confirmed in one organisation often reaches others days later. Without shared protection, each one meets it as something new.
Known bad domains and sign-in patterns reach your people before anyone has checked them.
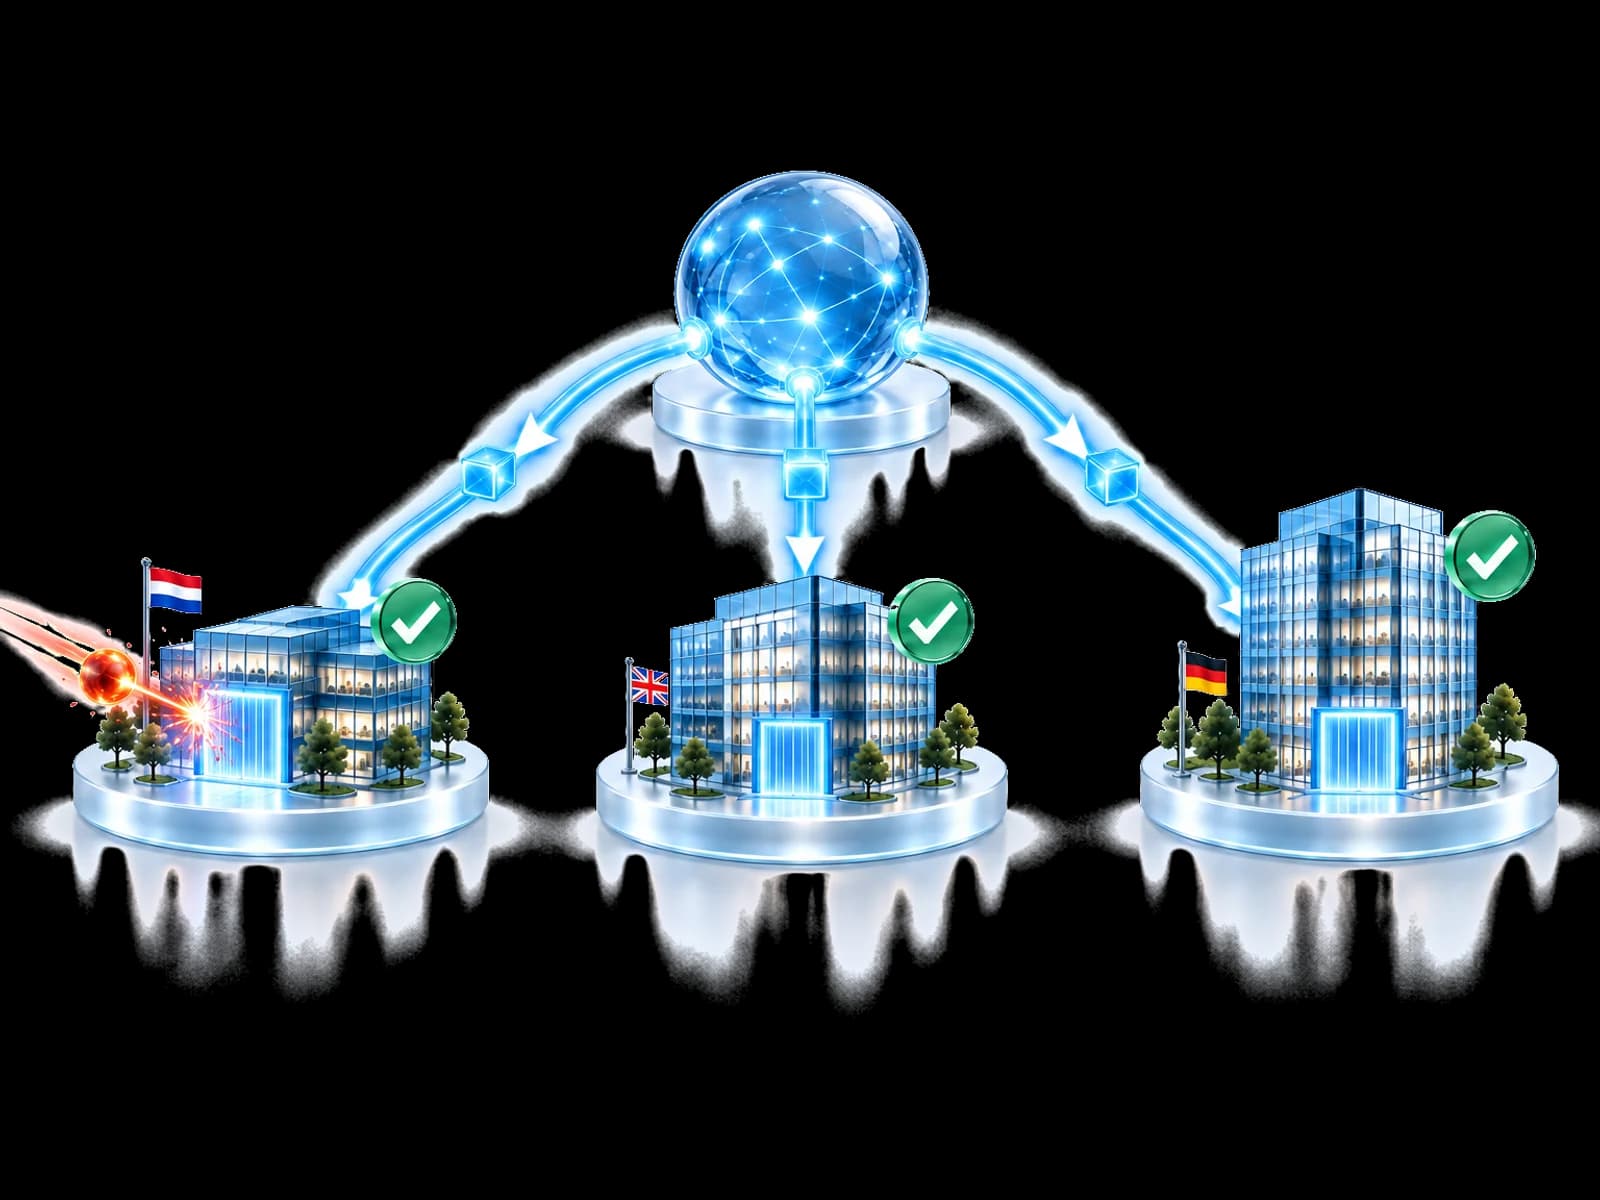
Validated findings can become protection in supported Microsoft sign-in, email and device controls in your tenant, where your policy, permissions and licences allow.
Tenant gate
Choose a connected security tool. UnifiedONE checks what your organisation can do before requesting a response.
Outcome: the identity route can be requested under tenant authority.
Illustrative flow. No customer data.
Every route remains conditional on tenant configuration, policy, permissions, licensing, connected-provider capability and available state read-back.
Provider acceptance is not proof that preventive protection is active.
Built for your team
Benefit from threats found elsewhere without researching them yourself.
Help raise the gate for eligible customers from one validated finding.
Apply known-threat protection consistently across business units.
Spend time on new threats, not on ones already confirmed elsewhere.
Questions
No. Front Gate Protection is preventive coordination, not a new gateway or replacement SOC. It is designed to carry validated defensive context to eligible identity, endpoint and mail controls already connected to the tenant.
Microsoft Entra ID is the connection, with Entra ID P1 or higher and consent from a Global Administrator. Email protection depends on each tenant's Microsoft services and licences. Microsoft Defender for Endpoint is integrated today; where it is in place, endpoint actions depend on onboarded devices and the released action set. The exact actions available still depend on tenant configuration, permissions and licensing.
The route stops and the missing capability remains visible. Front Gate Protection does not present an unavailable control as successful protection, and available paths can still be considered under local policy.
Only where the tenant's configured policy and authority allow it. A response may require approval, and every action remains conditional on permissions, an eligible connected control and licensing.
Defensive indicators, validation and confidence metadata may be shared according to the participation model. Users, mailboxes, files, investigations and tenant identity remain inside the tenant.
No. Validated intelligence can improve preventive protection only where the finding is relevant and an eligible local control, policy, permission and licence allow a response.
No. An accepted request is different from an observed protection state. Where the connected provider supports read-back, the resulting state can be checked; otherwise the limitation stays visible.
Carry validated findings to an eligible local control, under the tenant's own authority.
Preventive action remains conditional on local capability.Create your account and start your guided onboarding.