Same threat. Same investigation. Again.
Useful findings can get lost between customer investigations. The next team starts again.
Connected Intelligence. Collective Protection.
Connect Microsoft security signals with multi-vendor threat intelligence and cross-tenant knowledge. Turn what one environment learns into stronger protection across many.
Create your account and start your guided onboarding.
Community sharing is optional. Your connected tools keep working together when sharing is off.
Actions depend on policy, permissions, supported controls and licensing.
01 / The problem
Your team may already know the campaign. The next customer still needs that knowledge checked against their own environment.
Useful findings can get lost between customer investigations. The next team starts again.
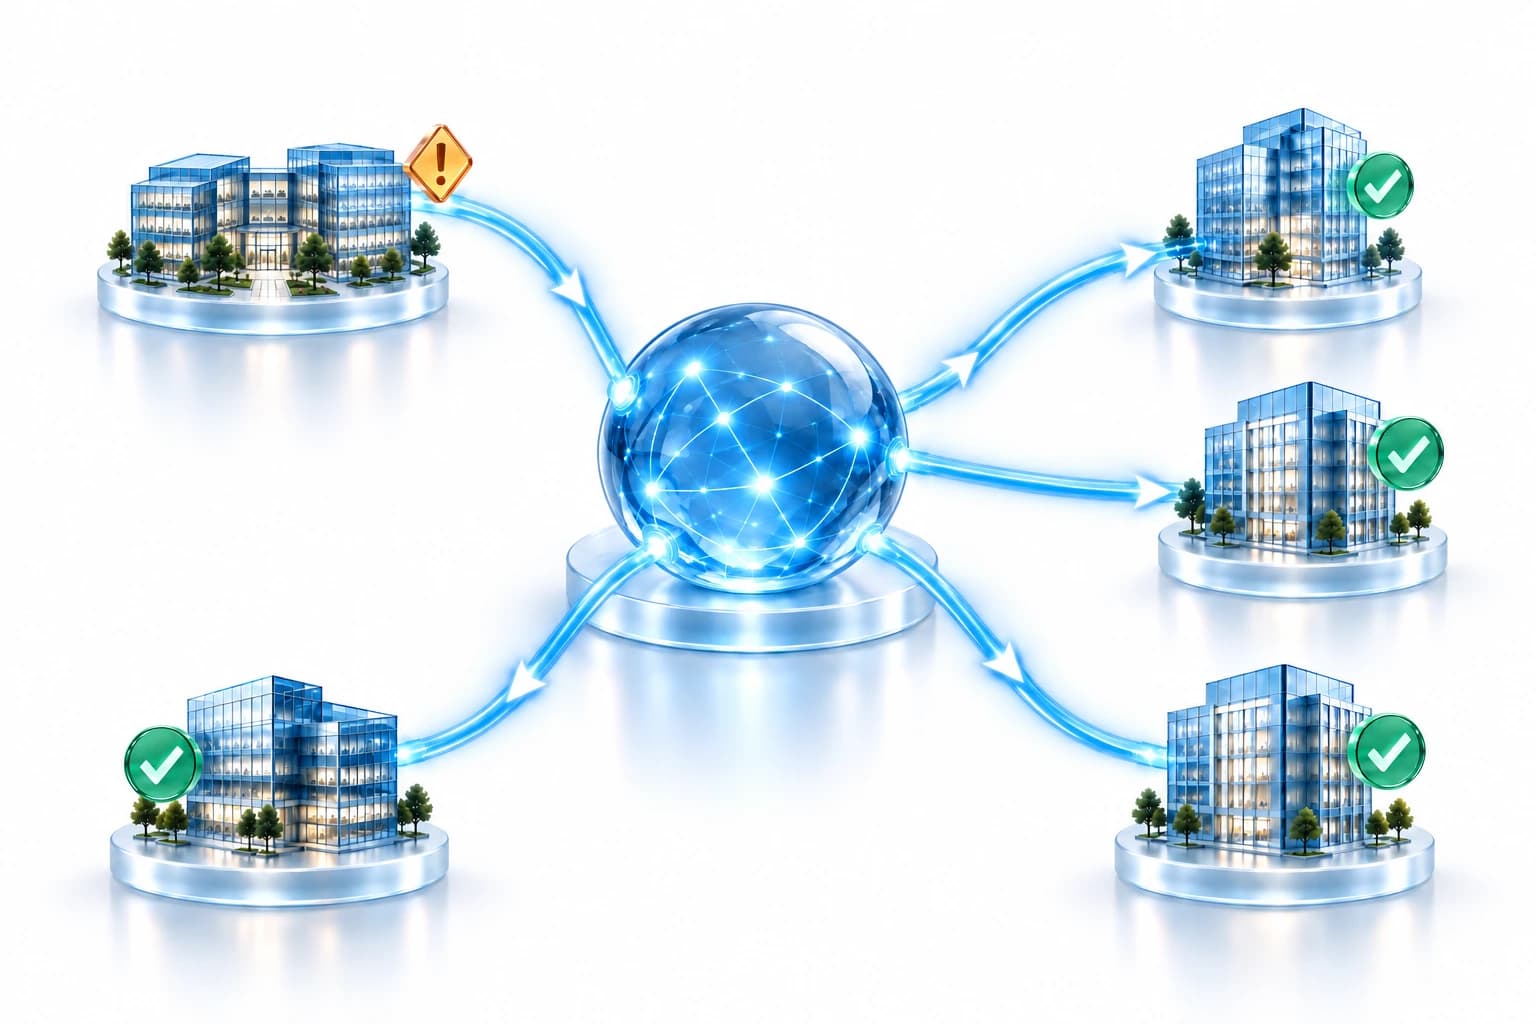
A validated finding gives another eligible customer a starting point for an approved response.

Example with connected controls and pre-approved policies. Industries, locations and user counts are illustrative.
Your Microsoft tools. UnifiedONE intelligence.
02 / The solution
Connect supported Microsoft signals with trusted intelligence and community findings. Check the evidence, then coordinate an approved response.
Review Microsoft signals alongside threat intelligence and community findings.
DCRE — Dynamic Confidence & Reputation checks the evidence and scores confidence.
Front Gate Protection uses your existing Microsoft controls where policy and capability allow.
03 / How it works
Follow one finding from discovery to a local response.
A threat is investigated.
The threat is confirmed.
Correlates and scores the finding.
Checks where else it applies.
The malicious domain is blocked through a connected security tool, using the validated finding from another organisation.
The same intelligence can lead to different outcomes. Actions depend on relevance, local policy, permissions, supported controls and licensing.
04 / Community Shared Defence
Participating MSPs can share useful findings across different toolsets. UnifiedONE validates the lesson so eligible Microsoft environments can use it under their own rules.
One organisation learns. The network gets stronger.
UnifiedONE integrates with your security ecosystem. We do not replace it.
Threat knowledge from different sources and security ecosystems strengthens the collective intelligence.
Every validated lesson can strengthen the wider participating network.
For connected Microsoft tenants, validated intelligence can become preventive protection through existing Microsoft security controls.
How Community Shared Defence works
A participating organisation or an integrated intelligence source detects a threat.
UnifiedONE correlates, scores and validates the intelligence before it becomes trusted knowledge.
Validated intelligence Correlated. Scored. Trusted.
Privacy-safe intelligence strengthens participating organisations through the collective defence network.
For connected Microsoft tenants, validated intelligence can be applied through the Microsoft security tools already in place.
Enforced today through Microsoft Entra ID, Microsoft Defender for Endpoint and Microsoft Defender for Office 365.
One threat. One lesson. A stronger network.
05 / Business value
Teams can reuse validated findings, see where protection applies and keep a clear record of approvals and gaps.
Use validated lessons from participating environments through the Microsoft security controls you already have.
Explore business protection ↗Reuse a validated finding across eligible customers while each keeps its own policy, controls and approval rules.
Explore provider solutions ↗Validated intelligence. Faster response. Spend analyst time on what is new, not on threats already investigated elsewhere.
Explore SOC Commander ↗Help eligible business units use each other's validated findings under their own policies.
Explore enterprise solutions ↗06 / Your protection. Your control.
Learn from threats seen elsewhere while keeping control of how your own organisation responds.
Review security and data handlingYour policy decides whether a response runs automatically, waits for your approval or only informs your team.
A response uses the controls and licences available in each environment. Confirm supported actions before connecting.
Sharing follows participation rules. Other organisations do not gain access to your environment.
No. We replace nothing. UnifiedONE works with the security tools you already use, adds validated intelligence and coordinates protection through the controls you already have.
No. UnifiedONE connects intelligence across different security ecosystems. Today, validated intelligence can be applied to connected Microsoft tenants through the Microsoft security tools they already use.
Yes. Small businesses and enterprises benefit from the same shared threat intelligence. The response available to each organisation depends on its connected tools, policies, permissions and licences.
Sharing defensive knowledge does not give other organisations access to your environment. Review the documented data-handling model for the scope and boundaries of participation.
Review data handling →Explore the platform and Microsoft integration pages for supported tools, permissions and deployment requirements.
Explore Microsoft integration →Connect what you know. Strengthen how you protect.
Create your account and start your guided onboarding.