Verdict by verdictConflicting
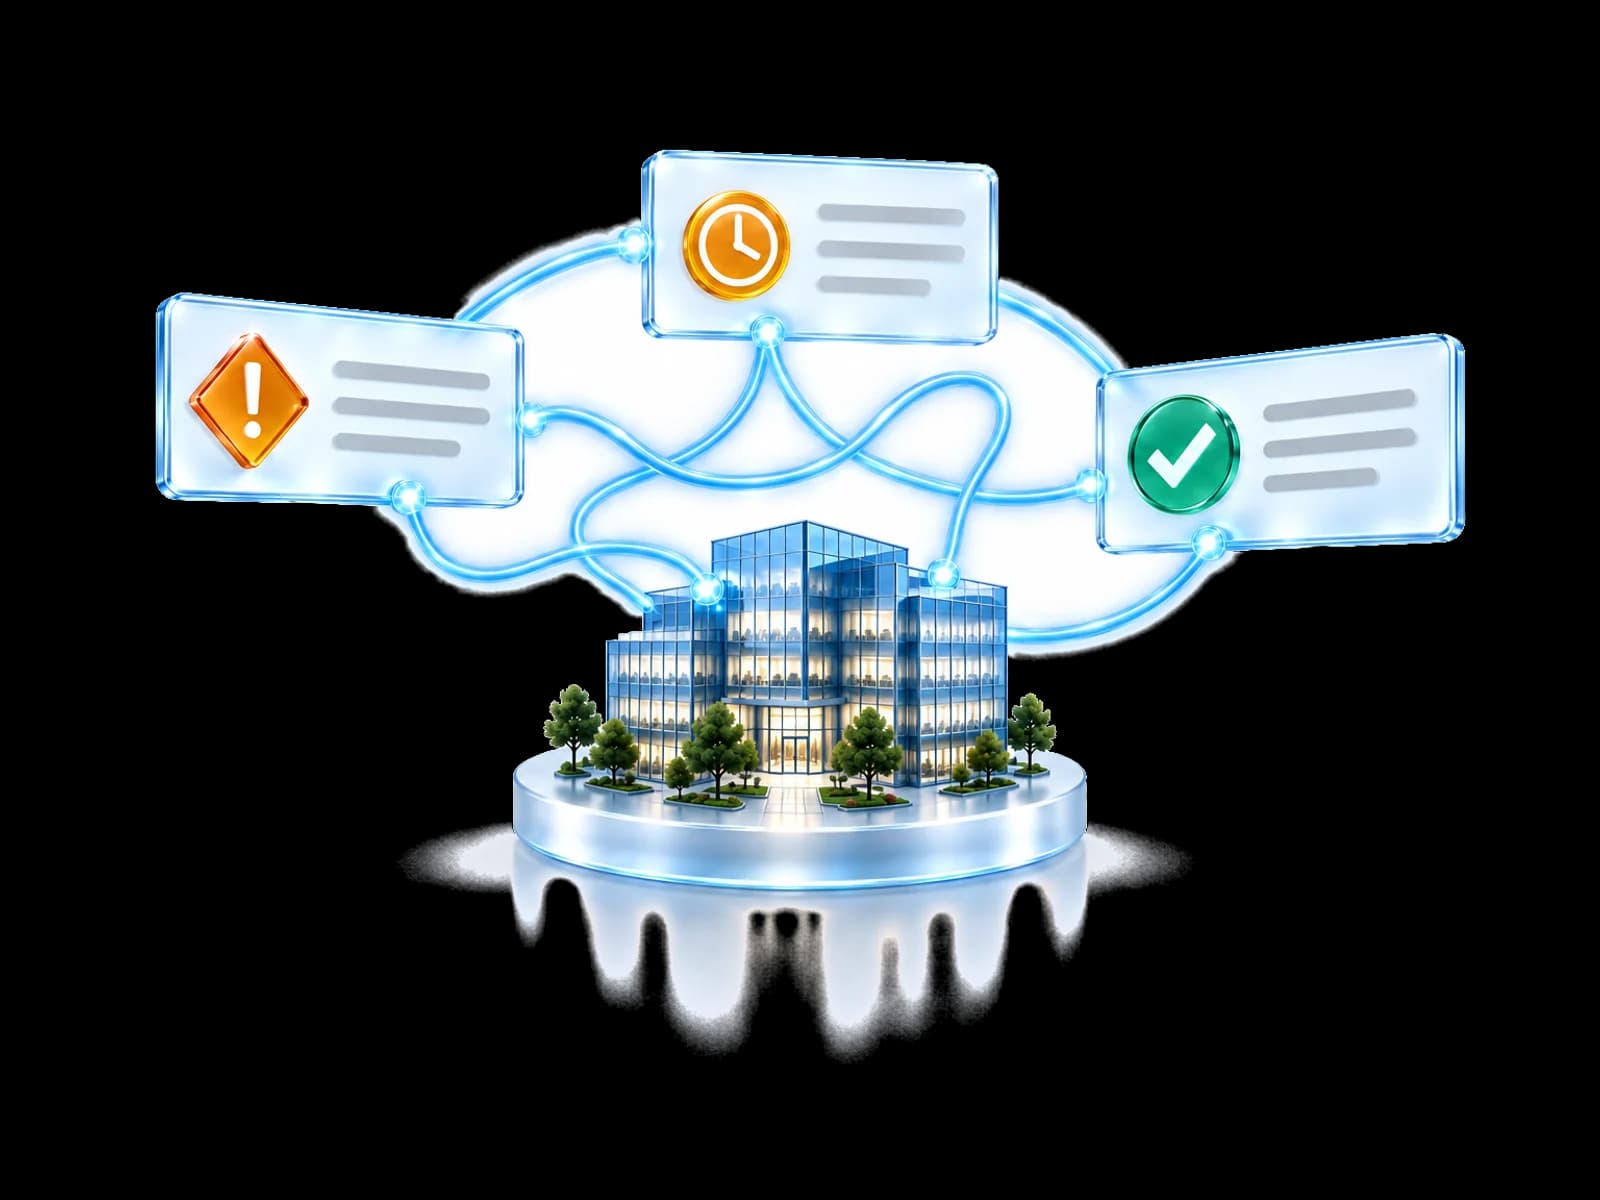
Conflicting verdicts, no clear answer.
Your team has to judge which source to trust, every single time.
Shared Defense Intelligence
UnifiedONE weighs Microsoft signals, MISP intelligence and community observations with DCRE — Dynamic Confidence & Reputation — so your team can act on what is confirmed and set aside what is not.
Less noise. More confident decisions.Create your account and start your guided onboarding.
The problem
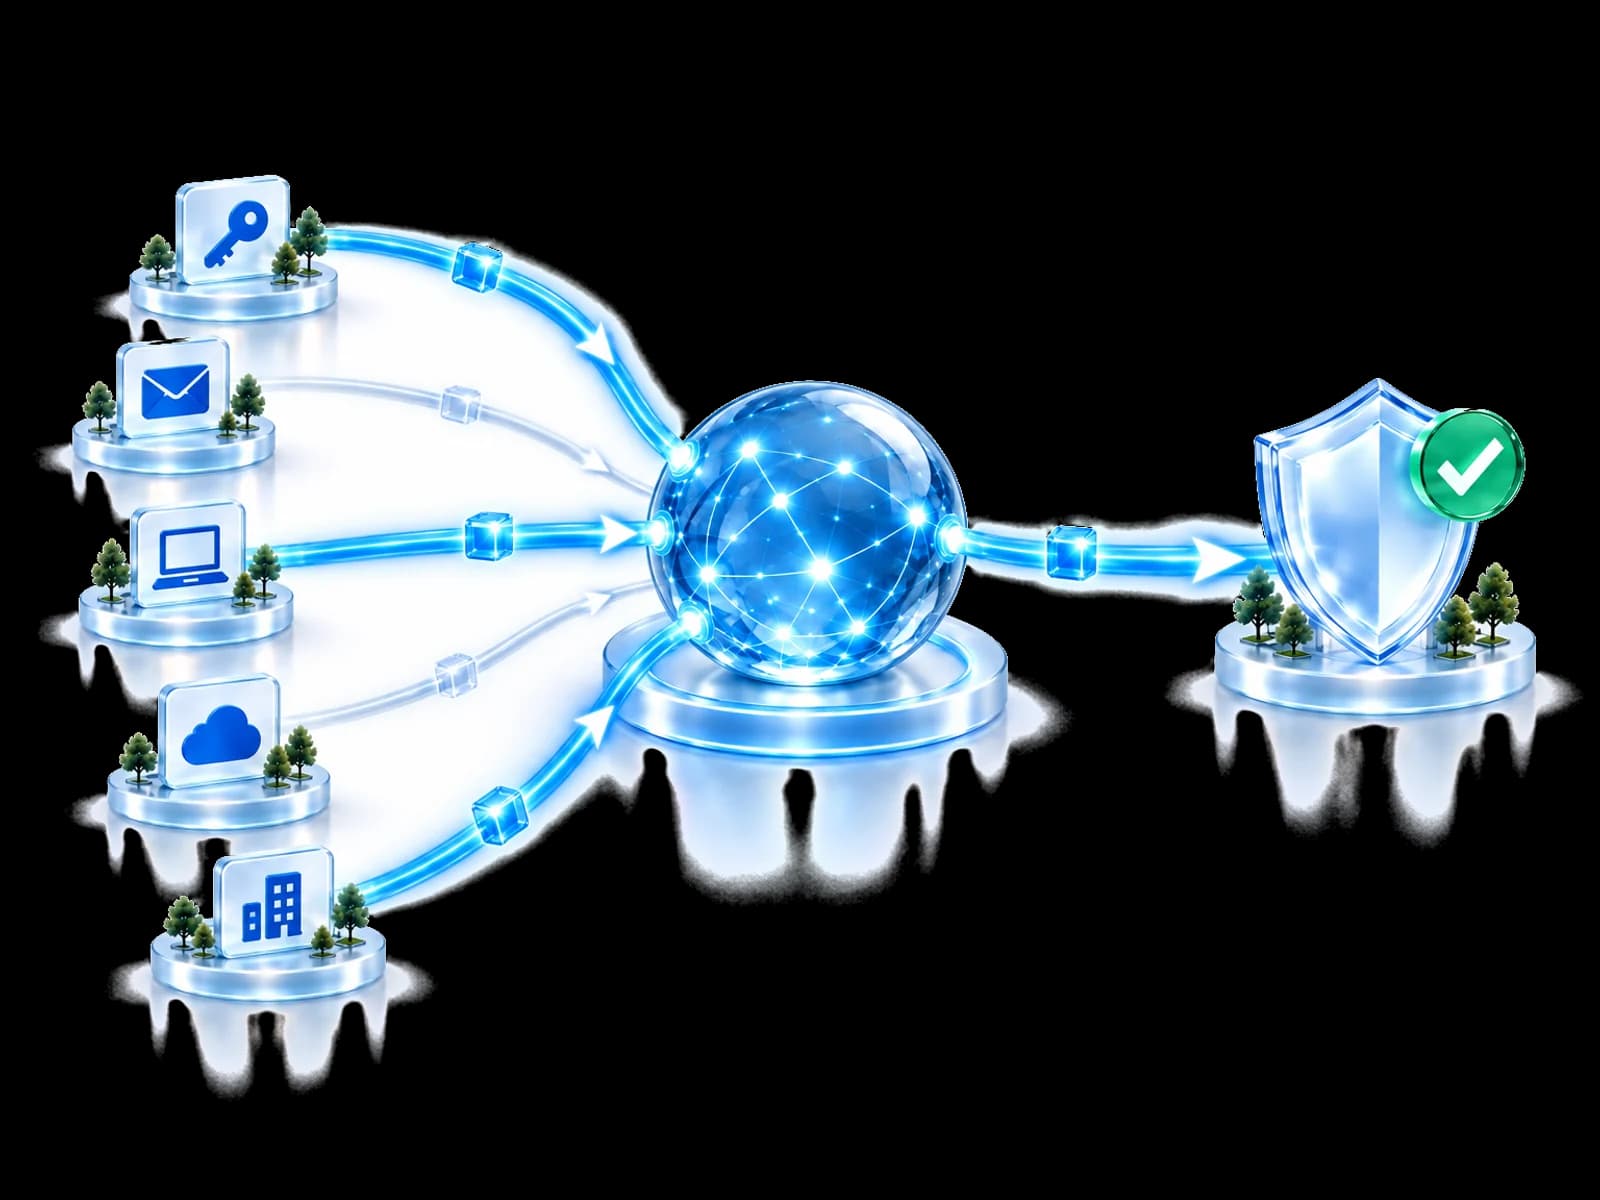
Each tool and feed gives its own verdict. Treat every one as urgent and you waste time; ignore them and you risk missing the real attack.
Your team has to judge which source to trust, every single time.
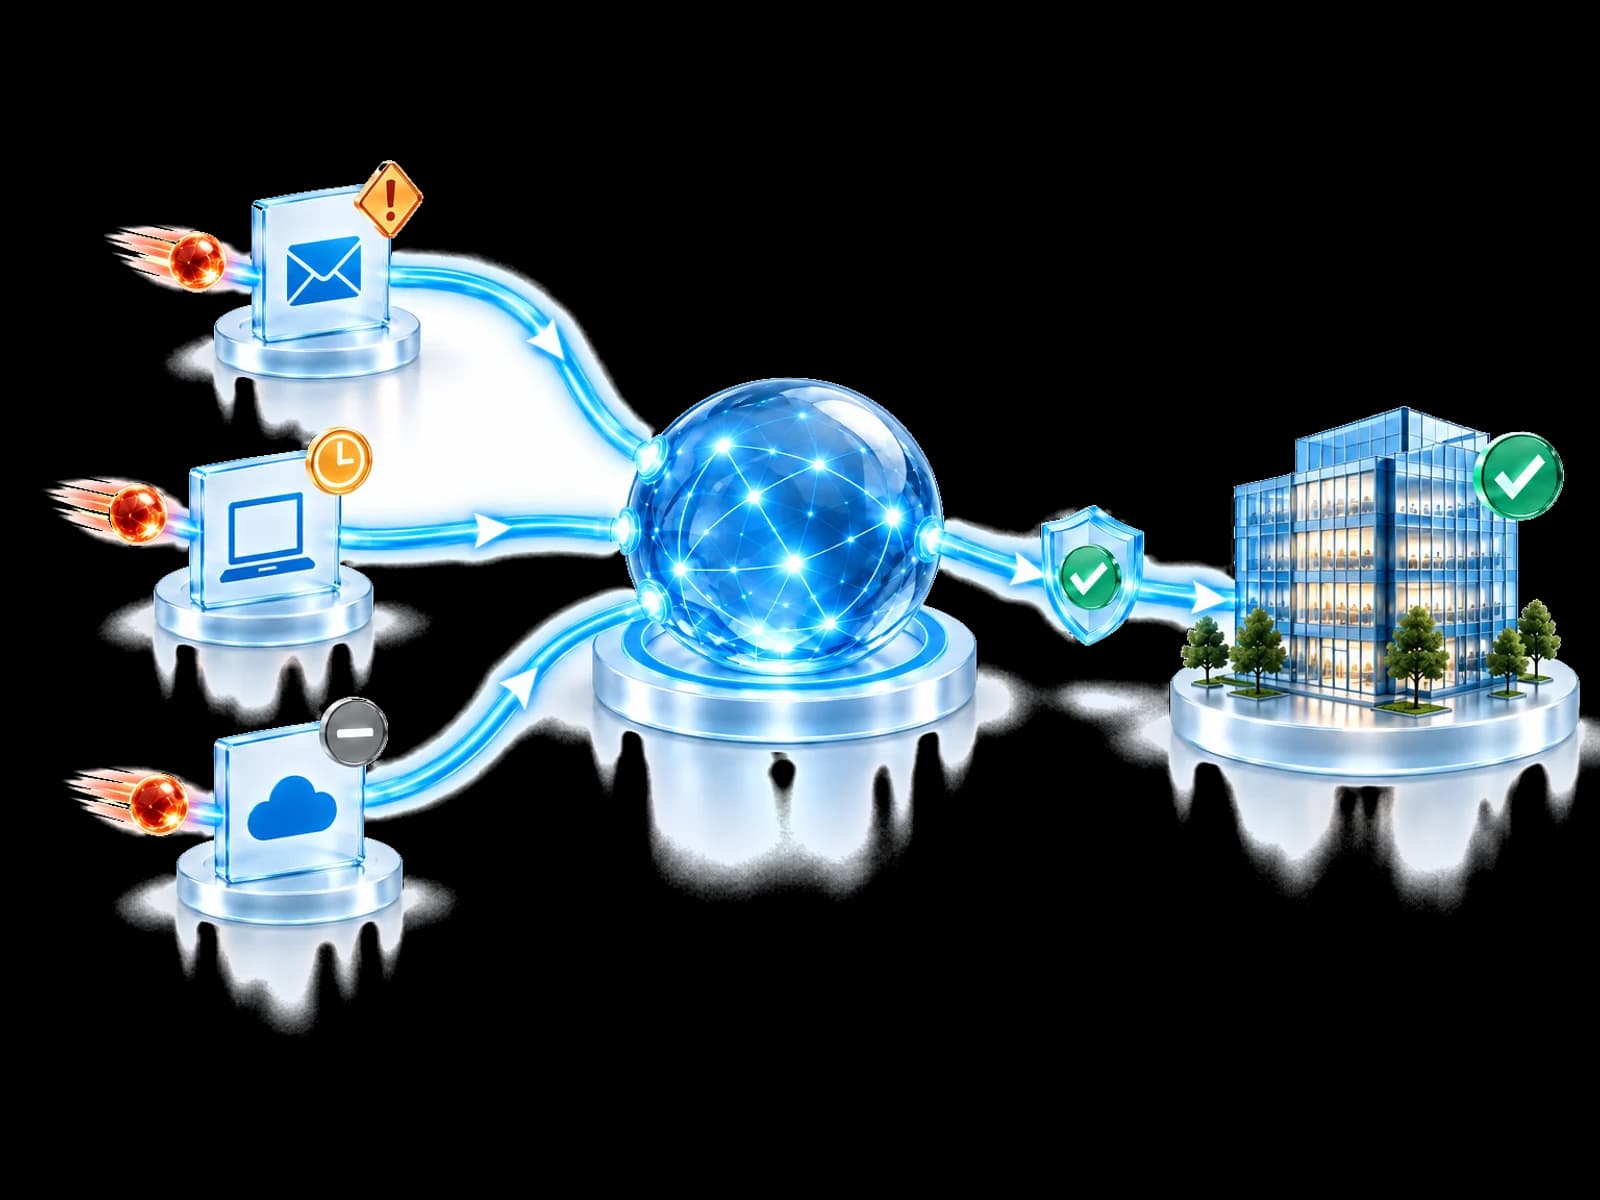
DCRE considers source reliability, age and contradicting evidence, so the recommendation shows why, not just what.
How it works
Inspect each source to see how it changes the review. No single observation decides the outcome.
This supports review because it is directly relevant to the protected environment. It is still one observation, not a final verdict.
Illustrative evidence. No customer record or live confidence score.
What happens next
Shared Defense Intelligence validates and explains the finding. It does not enforce protection itself or make the same action run everywhere.
The finding applies to this environment.
Local authority allows the hand-off.
A supported connected control can respond.
Required access and entitlement are present.
The Threat Intelligence Network correlates supported security signals, external intelligence and privacy-safe community observations. Dynamic Confidence & Reputation maintains confidence and reputation as validation, contradiction, recency and time change.
Built for your team
Get a clear recommendation instead of a pile of alerts.
Use one trusted assessment across customers instead of re-checking every alert.
Make consistent decisions with Microsoft, MISP and community evidence side by side.
See supporting and conflicting evidence before you act.
Questions
No. A feed gives you indicators to read and rank. Shared Defense Intelligence correlates supported sources, keeps supporting and contradictory evidence visible, and records why a finding deserves review.
The Threat Intelligence Network ingests, normalises, enriches and correlates supported observations. DCRE — Dynamic Confidence & Reputation maintains confidence and reputation as independent support, validation, contradiction, recency and time change. They are connected, not the same component.
Privacy-safe attacker indicators, validation, confidence and expiry metadata may be shared according to participation settings. Names, users, credentials, messages, files, raw records and tenant access remain local.
No. A finding must still be relevant to each participating environment, and local policy, permissions, connected controls and licensing decide whether any downstream response is available or approved.
Start your onboarding
Connect your security environment and review what supports each finding before a response is considered.
Create your account and start your guided onboarding.