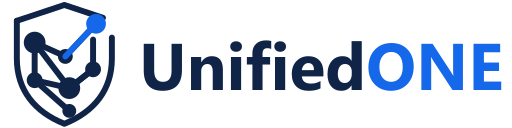
What can travel
- Malicious IP addresses, domains, URLs and file hashes
- A validated defensive lesson
- The context needed to judge relevance
Our vision
Attackers reuse what works across many organisations at once. Our vision is a community where a threat validated in one organisation helps protect the others, while each keeps its own data, policies and decisions.
Knowledge travels. Authority stays with each organisation.
Create your account and start your guided onboarding.
A lesson informs participating organisations where it is relevant. Actions depend on local policy, permissions, connected controls and licensing.
The starting point
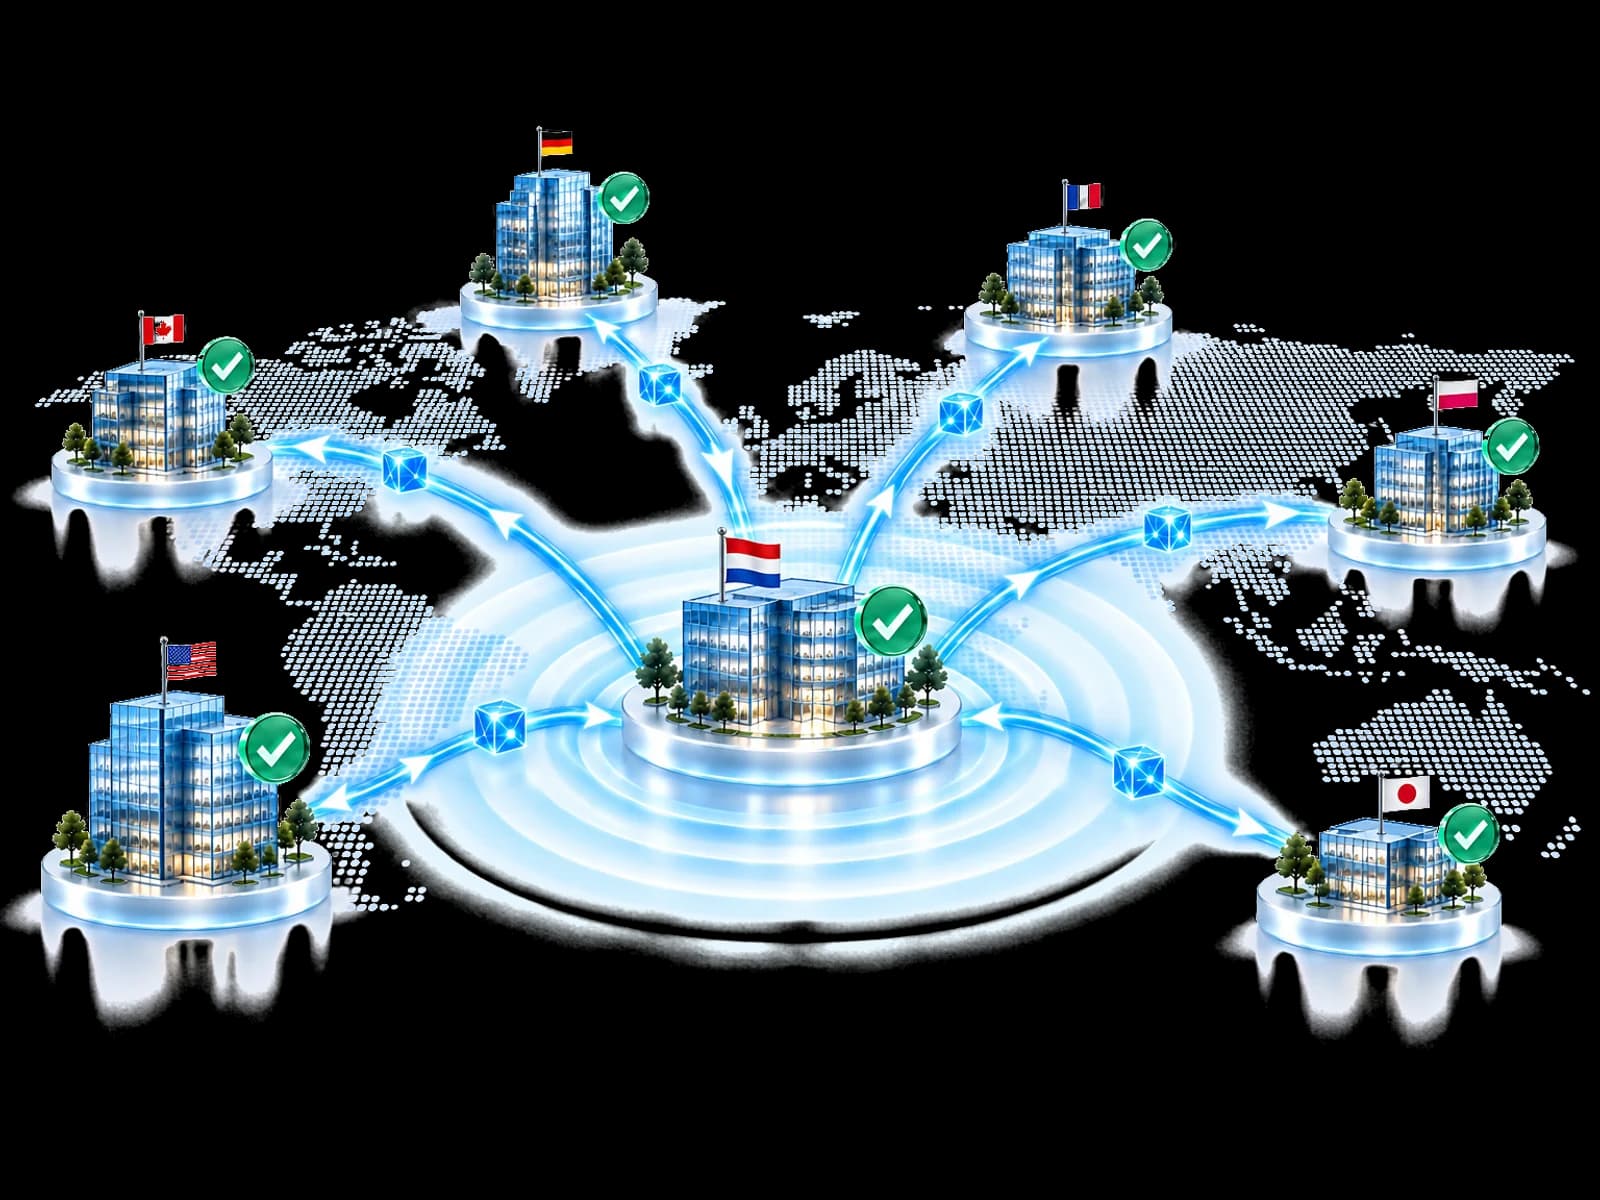
Most lessons stay inside the organisation that learned them. Four questions decide whether a lesson can safely help anyone else.
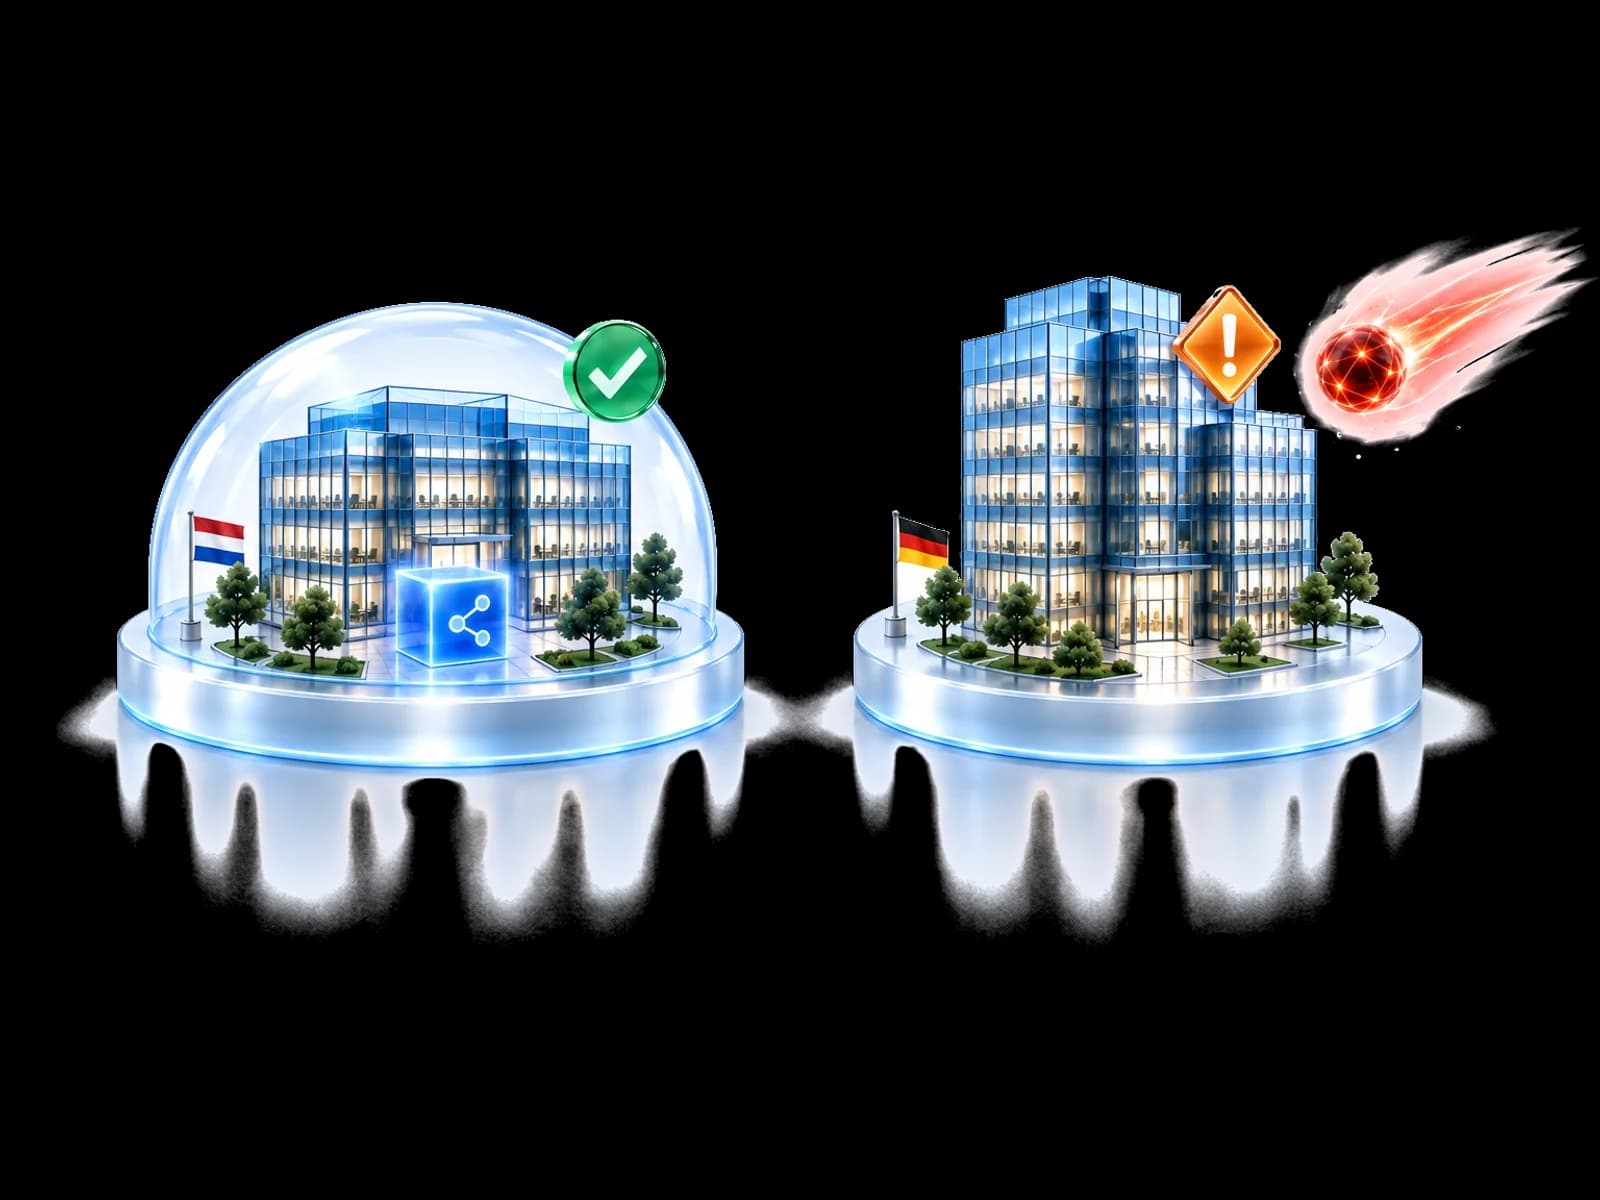
Today: What did another defender discover?Findings usually stay inside the team that made them.
In the community: A validated finding can inform other participants where it is relevant.
Today: Was the lesson checked before it travelled?Unverified warnings create noise and wear down trust.
In the community: Findings are assessed with DCRE — Dynamic Confidence & Reputation before they are shared.
Today: Does it matter here?Generic threat feeds rarely say whether a threat applies to you.
In the community: Relevance is checked against each organisation's own environment.
Today: What does local policy allow next?Automatic action without consent would take control away.
In the community: Each organisation's policy decides: apply, ask for approval or record the gap.
A lesson's path
The shared part is a defensive lesson. What happens with it is always up to the organisation that receives it.
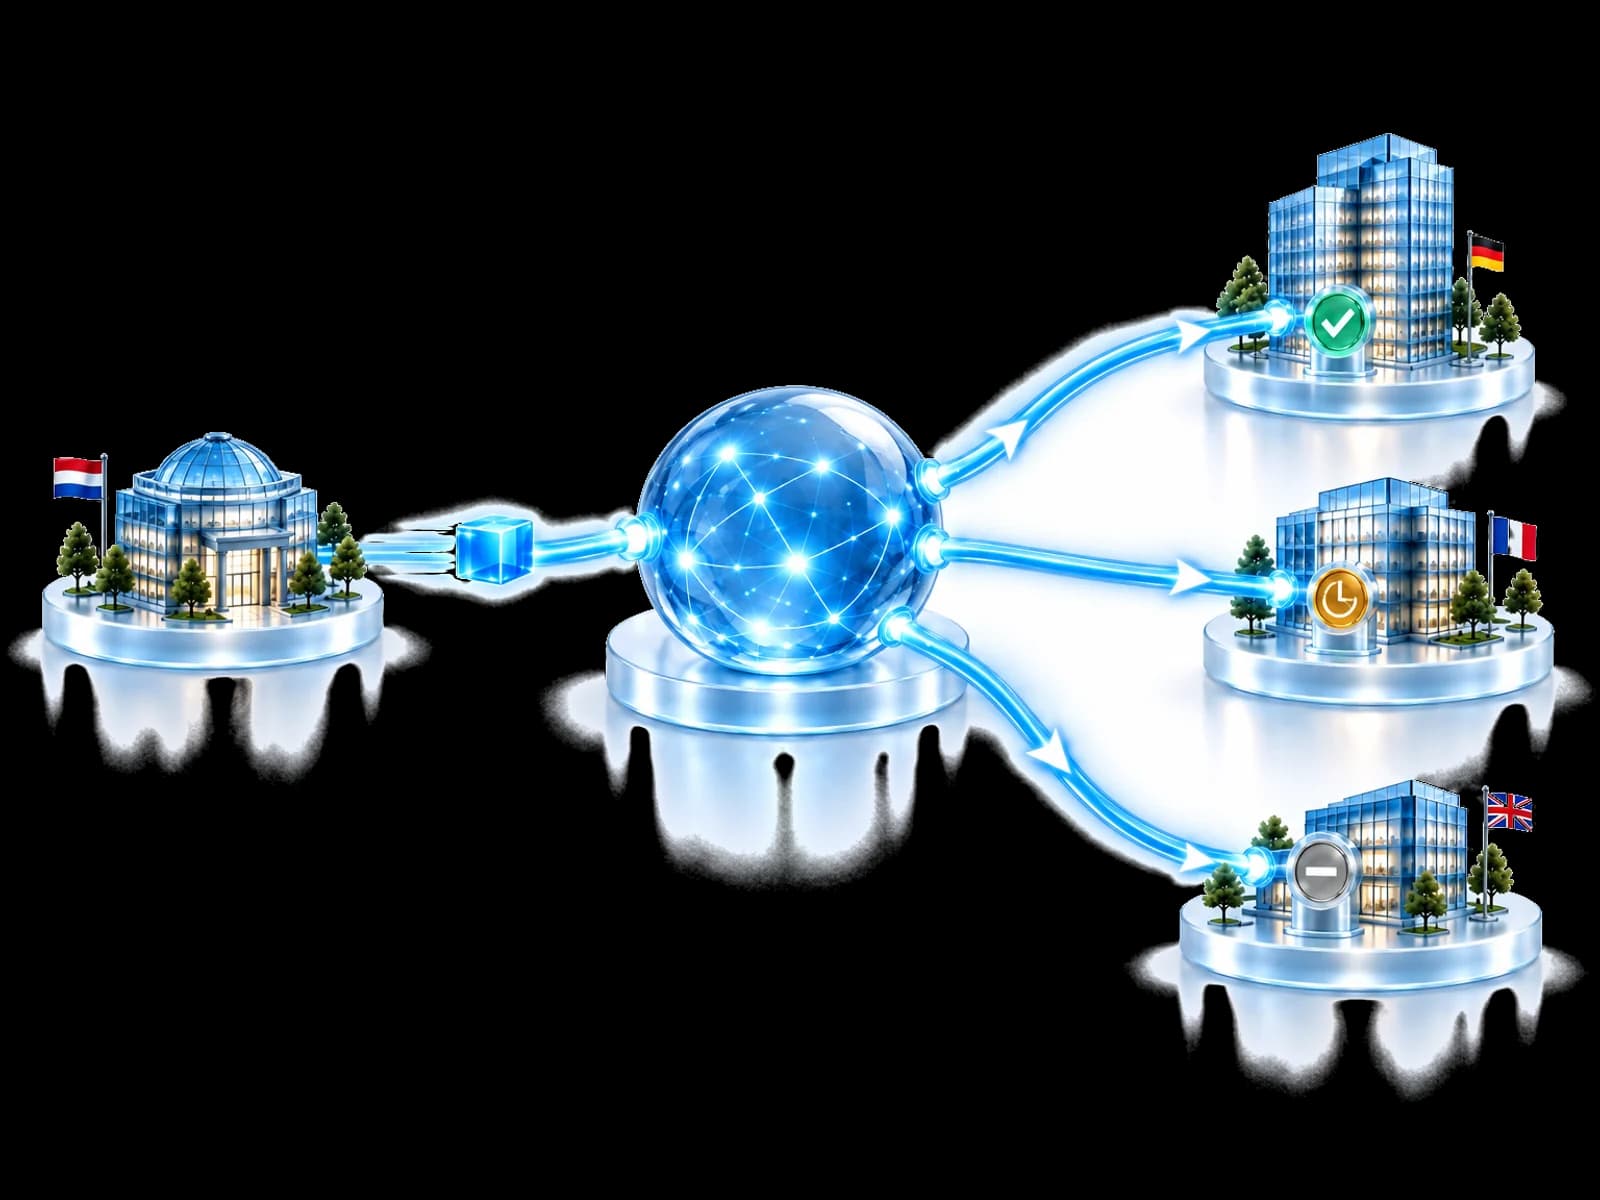
A participating organisation spots suspicious behaviour or confirms a threat.
The finding is checked, stripped of identity and personal data, and shaped into a lesson others can assess.
Participants where the lesson is relevant receive it as extra defensive context.
Each organisation's policy decides whether and how to act with its own controls.
What happens next
Pick an organisation and see why the same validated lesson leads to a different result.
Choose an organisation
B's policy allows automatic action for validated phishing domains, and its email control is connected.
Outcomes depend on relevance, local policy, permissions, supported controls and licensing.
The boundary
Taking part makes a useful lesson available. Every environment stays independent.
Knowledge moves through defined participation and governance, never without limits.
A lesson informs your next step. Your policy decides what happens.
Waiting approvals and missing controls are never reported as protection.
Who it helps
Taking part does not require every organisation to work the same way.
A feed delivers indicators. UnifiedONE validates a finding, checks whether it is relevant to each organisation and coordinates a response only within that organisation's policy.
No. Sharing defensive knowledge does not give another organisation access to your environment. Names, users, email content and files are not shared.
Only when your policy allows it. Otherwise the action waits for your approval, and a missing control is shown as a gap.
DCRE means Dynamic Confidence & Reputation. It weighs source reliability, recency and contradictory evidence before a lesson can be considered for sharing.
From idea to practice
Join the community to start guided onboarding, or see how the platform carries a lesson from discovery to your own decision.
Create your account and start your guided onboarding.