For enterprise security teams
Many tools and business units. One governed decision.
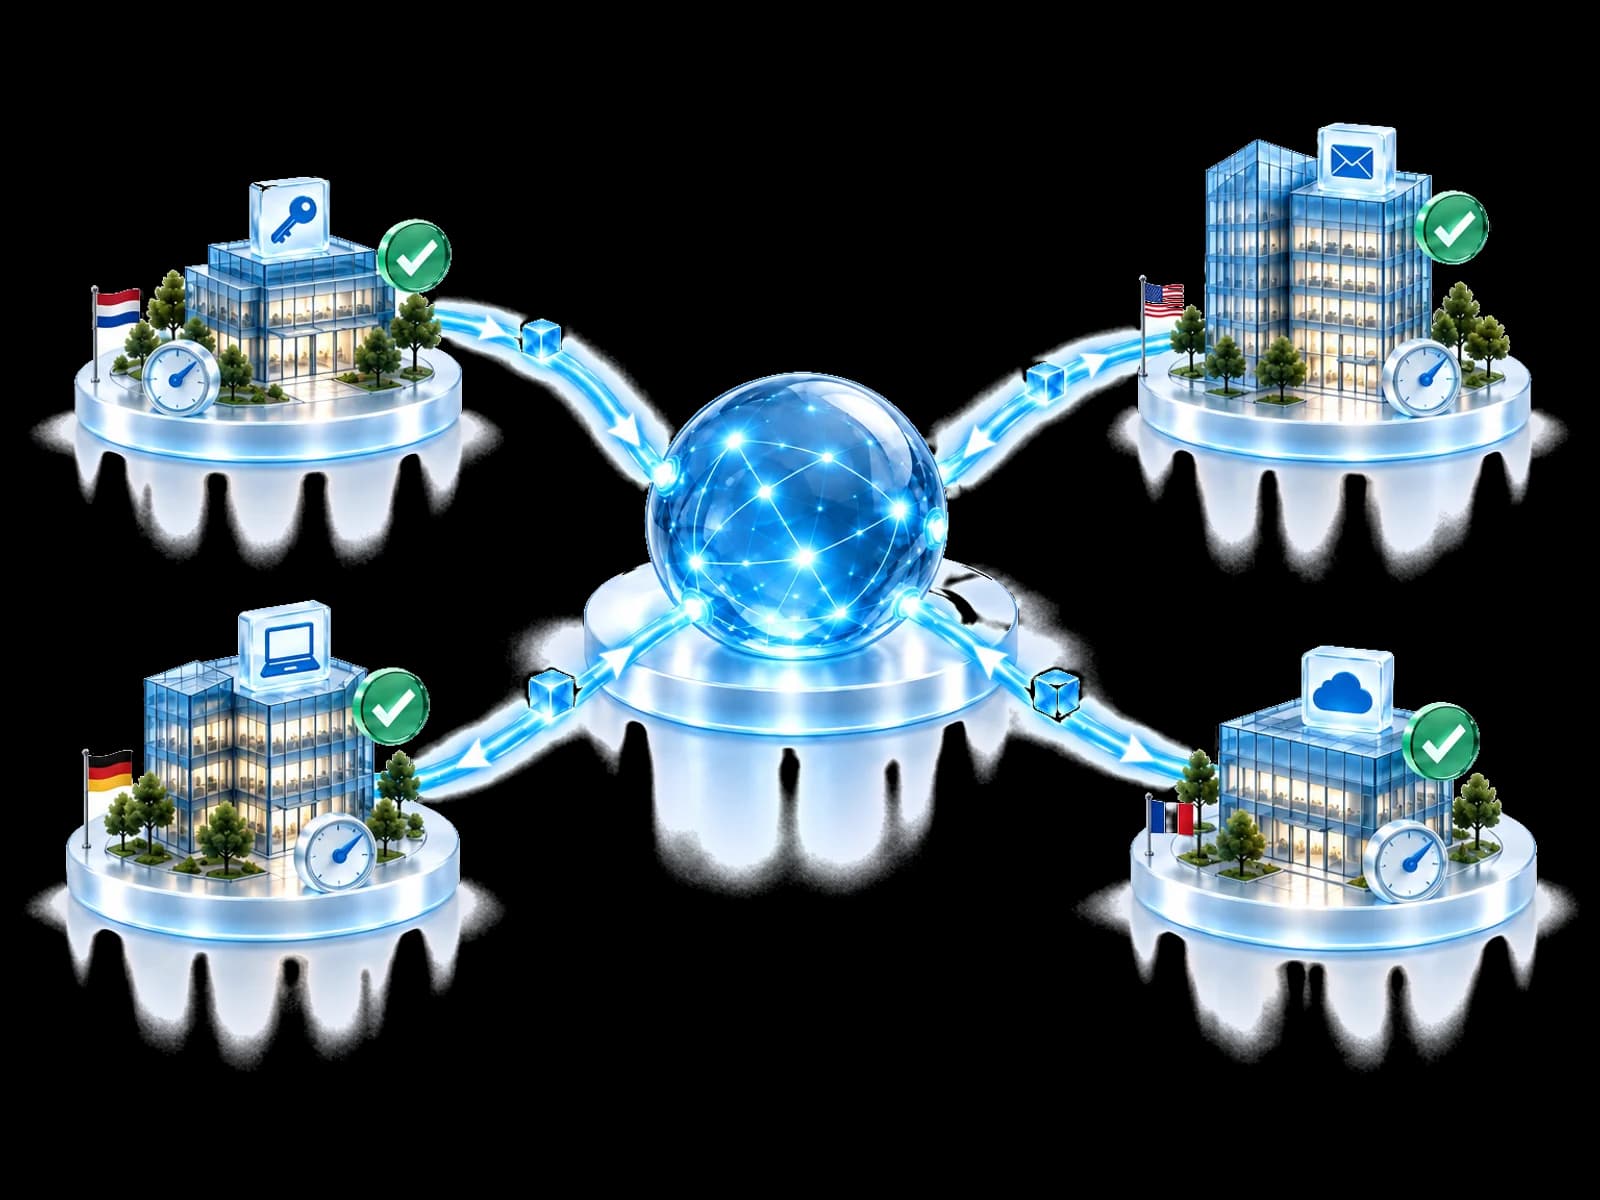
Different business units run different tools and processes. UnifiedONE connects their security evidence, helps teams reach a consistent decision and coordinates the response through existing controls, under local policy and approvals.
Consistency across the estate, without flattening local authority.
Create your account and start your guided onboarding.
Actions depend on local policy, permissions, supported controls and licensing.
- Built in the Netherlands
- Available on Microsoft Marketplace
- Works around your existing tools
- Local policy stays in force
The problem
Your estate has signals. Your team still needs a decision.
Every tool sees part of an attack. None of them tells the whole story or holds every unit to one standard.
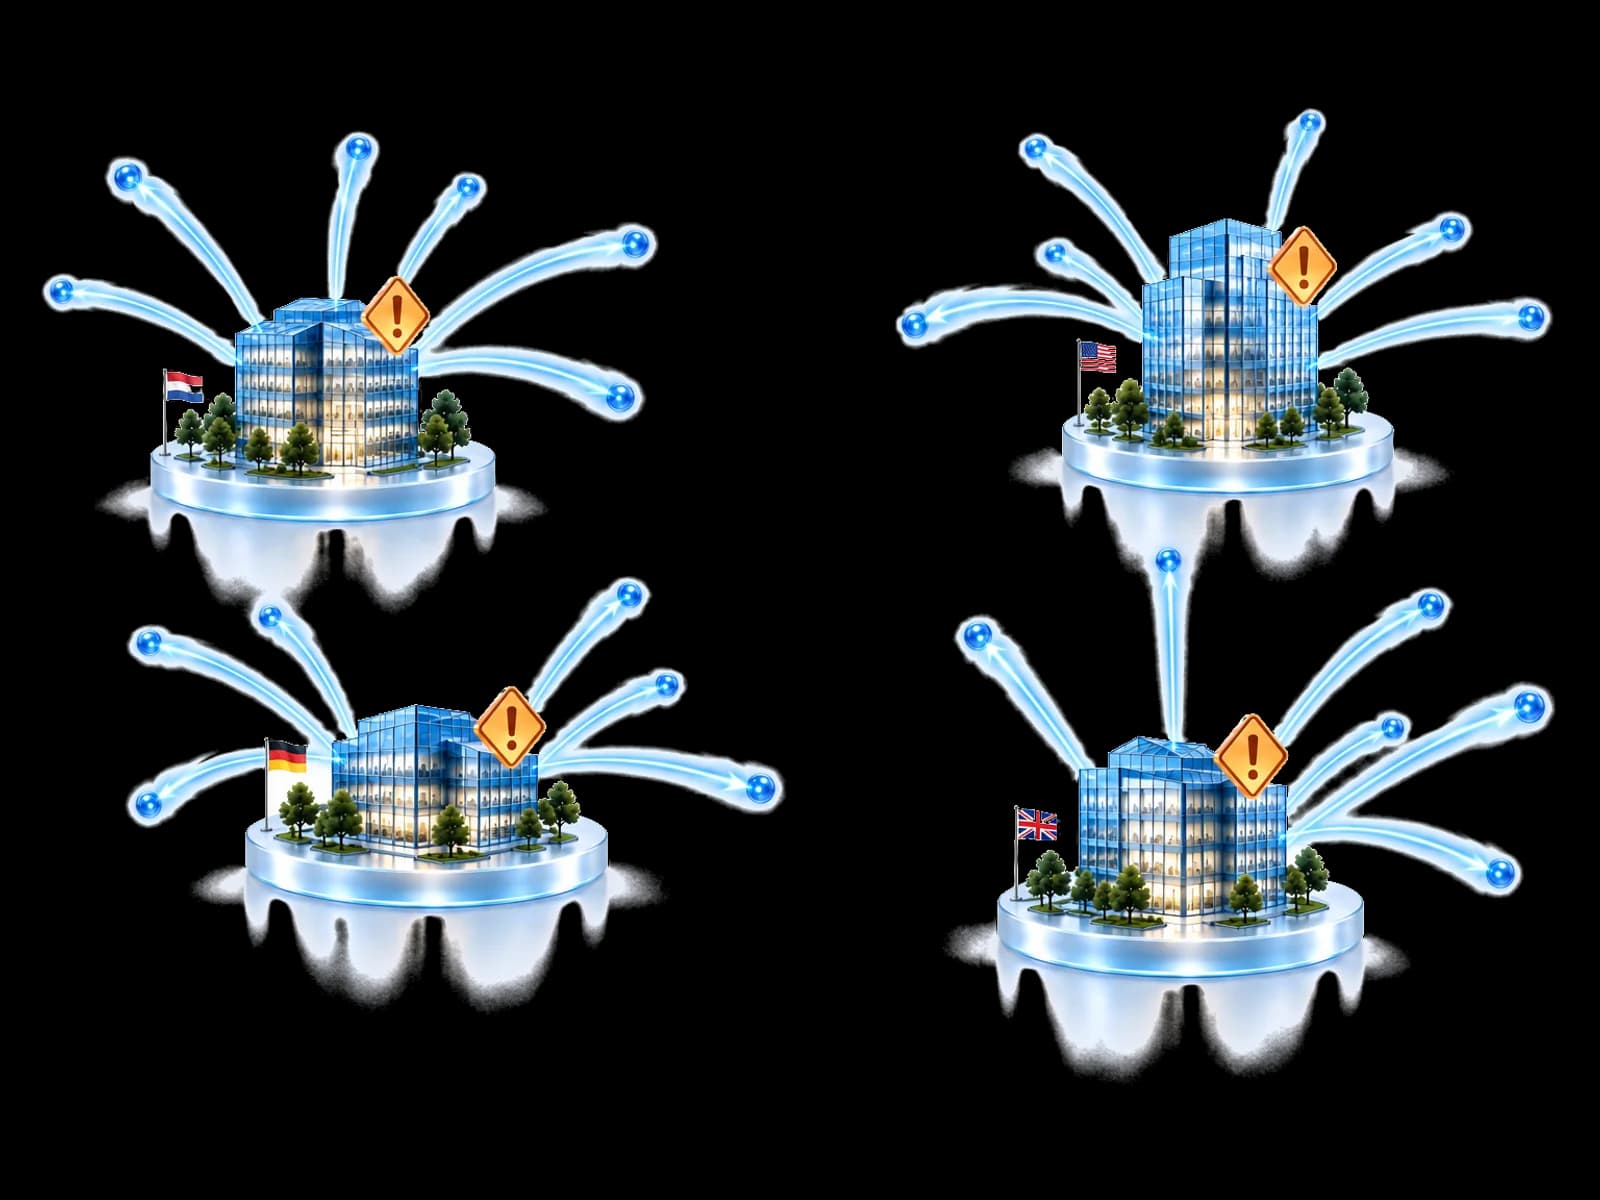
Each console alone: Endpoint consoleSees a blocked sign-in on one laptop. Cannot tell whether the same actor reached email.
With UnifiedONE: Connected with identity and email evidence in one case.
Each console alone: Identity consoleSees failed sign-ins from an unfamiliar network. Cannot tell whether a device was touched.
With UnifiedONE: Assessed against device and community evidence.
Each console alone: Email consoleQuarantines a message for one mailbox. Cannot tell whether another unit received it.
With UnifiedONE: Checked for relevance across business units.
Each console alone: Your SOCReconciles several consoles by hand before anyone can act.
With UnifiedONE: Works from one decision record with a clear next step.
How it works
From scattered evidence to a governed response.
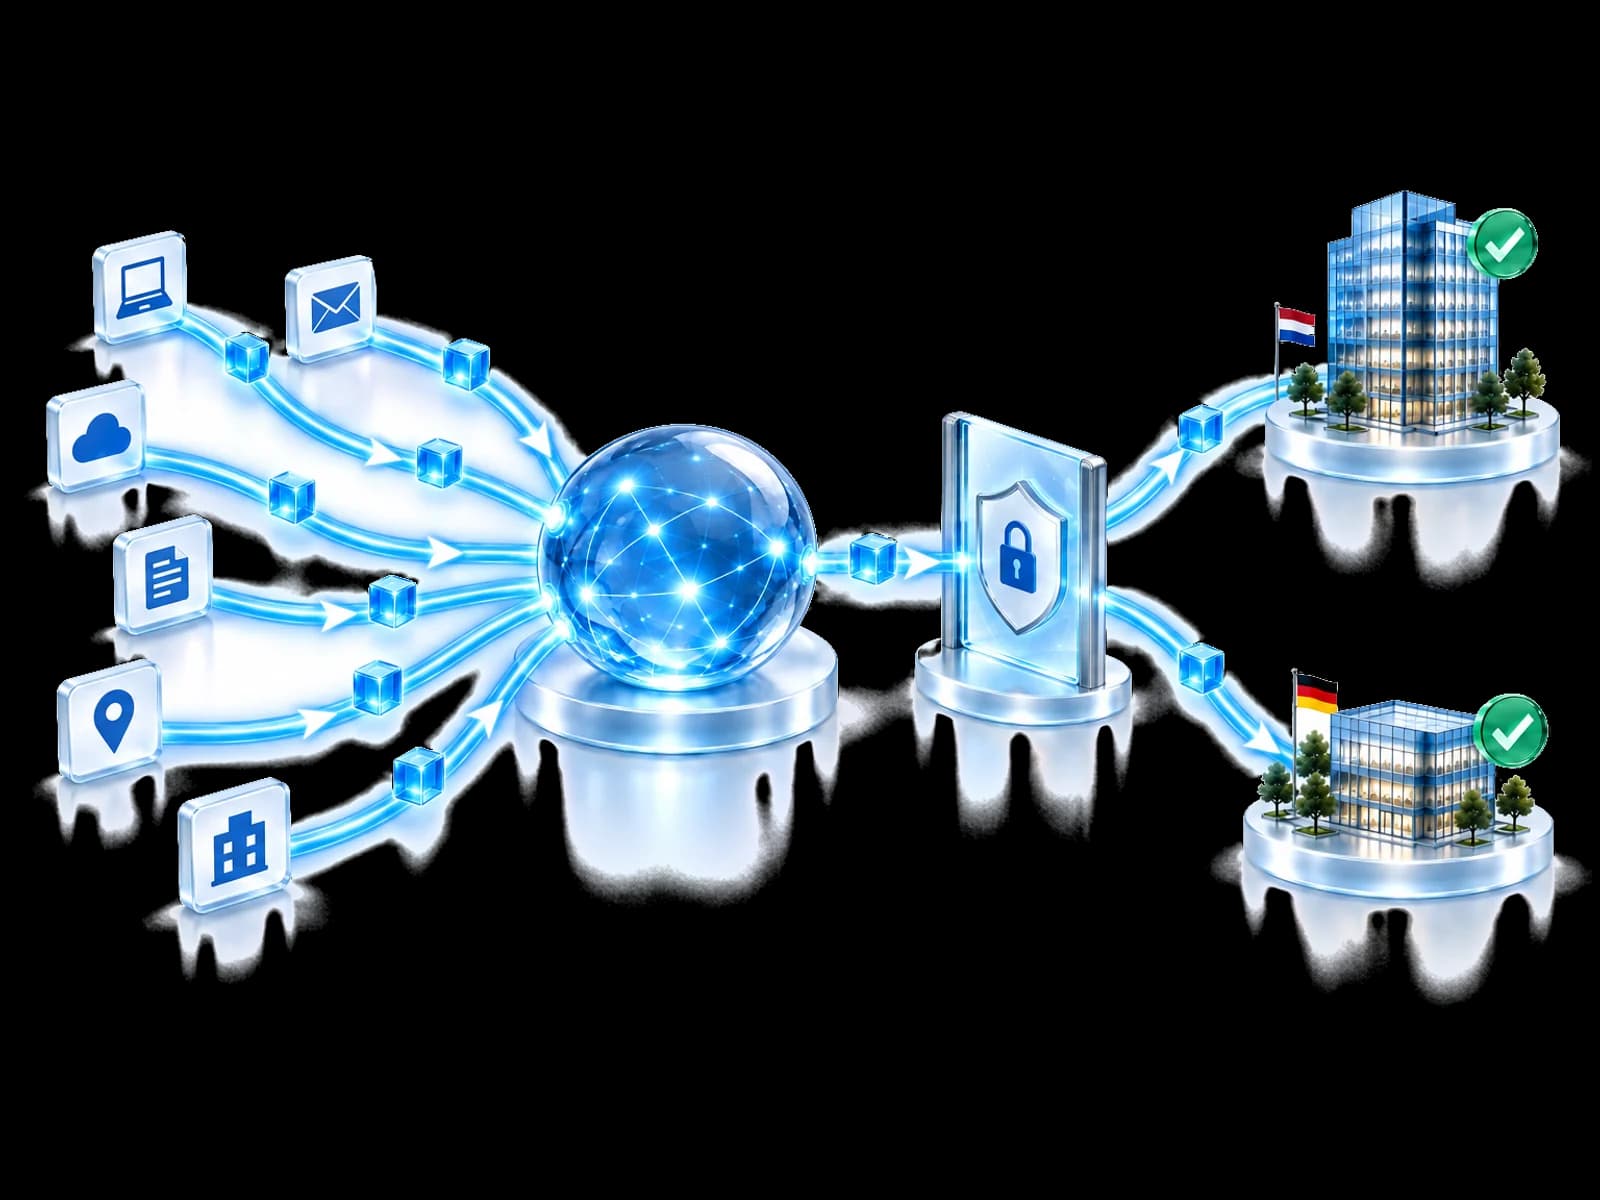
Every decision follows the same reviewable path, so it can be explained afterwards to the board, an auditor or an insurer.
- 1
Connect the evidence
Signals from endpoint, identity, email and cloud tools come together in one case.
- 2
Validate the threat
UnifiedONE assesses the finding with DCRE — Dynamic Confidence & Reputation and community evidence.
- 3
Check relevance and policy
Each unit's exposure, policy and available controls are checked before anything runs.
- 4
Coordinate the response
Eligible actions run through existing controls, or wait for the right approver.
- 5
Keep the evidence
The rationale, approvals and outcome stay with the record for later review.
The protection outcome
Consistency does not mean identical action.
Select a business unit to see how one validated decision meets different local conditions.
Select a business unit
Policy allows automatic action for this class of threat, and the identity and email controls are connected.
Outcomes depend on relevance, local policy, permissions, supported controls and licensing.
Business value
Govern the estate. Explain it to the board.
Security leaders need consistent decisions they can defend, not another console to watch.
Consistent standards
Hold every business unit to one validated decision while local authority stays intact.
Clearer decisions
Analysts start from connected evidence instead of reconciling consoles by hand.
Evidence for the board
Rationale, approvals and outcomes stay together for audit, board and insurer questions.
More from existing investments
Coordinate through the tools you already run instead of adding another one.
Create your account and start your guided onboarding.
Governance and sovereignty
Central insight. Local authority.
Built in the Netherlands and designed around European privacy expectations. Every unit keeps the final say over its own environment.
Review security and data handlingLocal policy decides
Each unit's policy decides whether an action runs automatically or waits for approval.
Only attacker indicators travel
Names, users, content and files are not shared between environments.
Gaps stay visible
Unavailable controls and pending approvals are recorded, never shown as protection.
Does UnifiedONE replace our SIEM, XDR or SOC?
No. It adds validated intelligence and coordination around the tools and teams you already have. Your SOC keeps its tools and its authority.
Can business units keep different policies?
Yes. Policy, permissions and approvals are set locally. One validated decision can lead to different outcomes in different units.
How do we show decisions to auditors or the board?
Each decision keeps its evidence, rationale, approvals and outcome together. Board-Ready Evidence and Control Fabric turn that record into reviewable reporting.
What leaves our environment?
If you take part in the wider community, only attacker indicators such as malicious domains, IP addresses, URLs and file hashes can be shared. Names, users, content and files stay in your environment.
Which environments does UnifiedONE work with?
UnifiedONE works with Microsoft environments, including Entra ID, Defender, Intune and Sentinel. Talk to us about the rest of your estate and what each connection supports.
Next step
Map the decision to your environment.
Join the Community to start guided onboarding, or bring your stack, business units and obligations to a conversation with our team.
Create your account and start your guided onboarding.