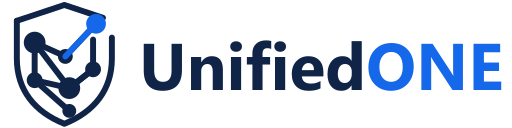
What can be shared
- Malicious IP addresses
- Domains and URLs
- File hashes
- Validated campaign context
For MSPs & MSSPs
Your customers keep the endpoint security they run today. Whether a customer fits depends on its Microsoft tenant, not its endpoint brand.
Your customers keep their Microsoft tools, licences and approval rules.
Create your account and start your guided onboarding.
Actions depend on each customer's policy, permissions, connected controls and licensing.
The problem
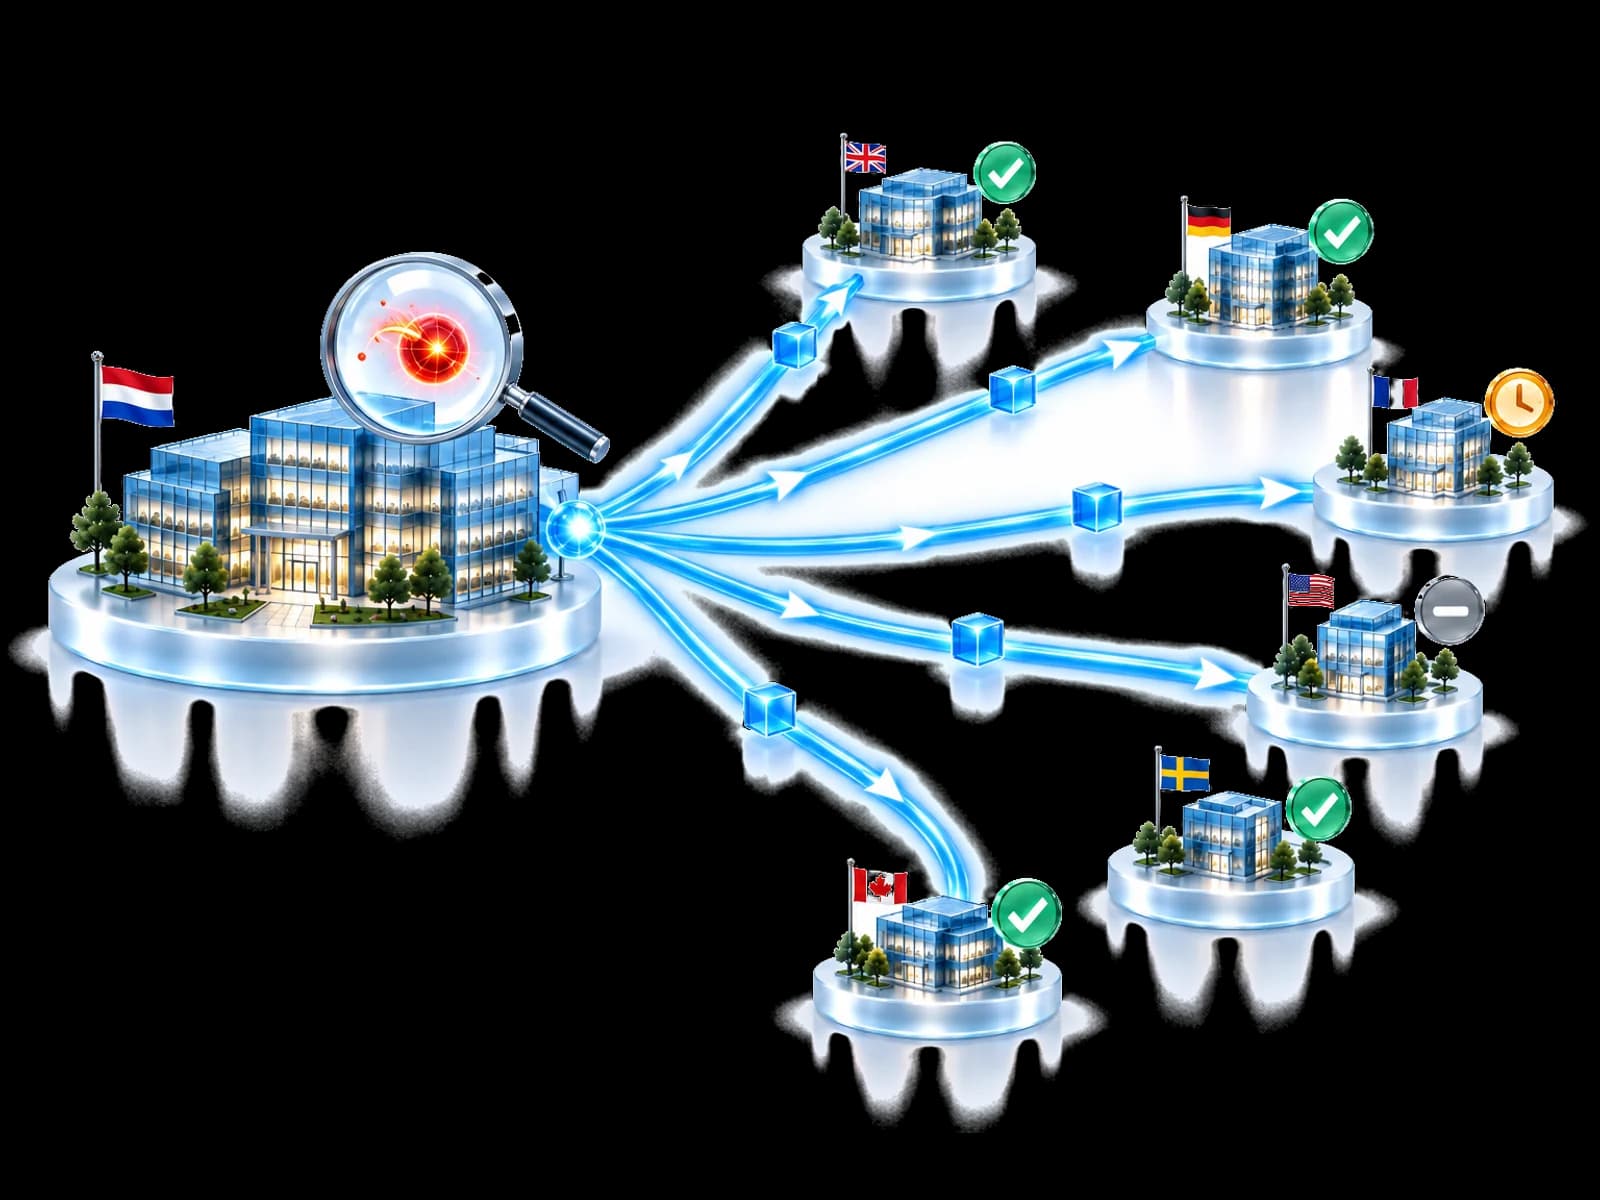
A campaign reaches another customer. Your team has already investigated it. That work should be useful again.
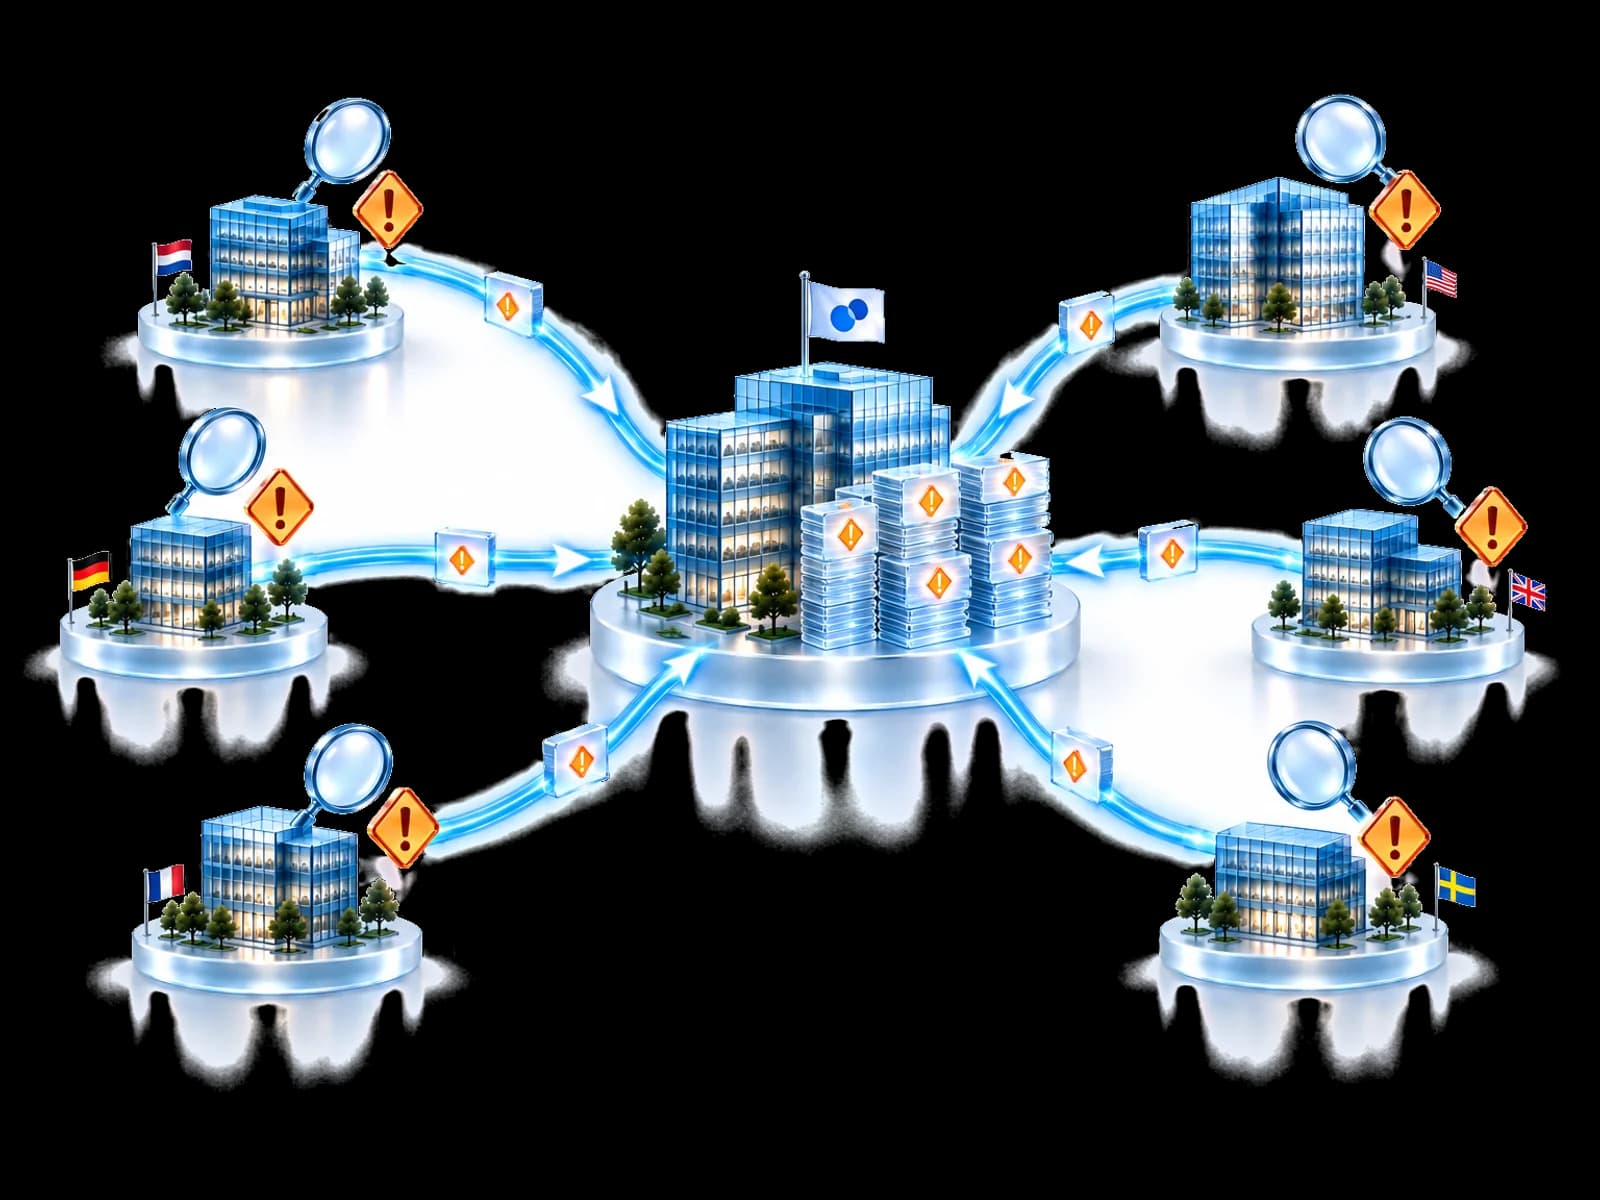
Today: The same campaign is investigated again in every customer portal.
With UnifiedONE: One validated finding can inform other eligible customers where it is relevant.
Today: Senior analysts spend their day on repeat, low-level alerts.
With UnifiedONE: Analysts spend their time on the cases that need local judgement.
Today: Checking tenant health means opening separate customer views.
With UnifiedONE: Review customer tenant health and baseline scores in one MSP dashboard.
Today: Every new customer adds the same investigation work again.
With UnifiedONE: Reuse investigation work as your customer base grows.
How it works
Your MSP account is reviewed before you connect customer tenants. Each customer keeps its own response rules.
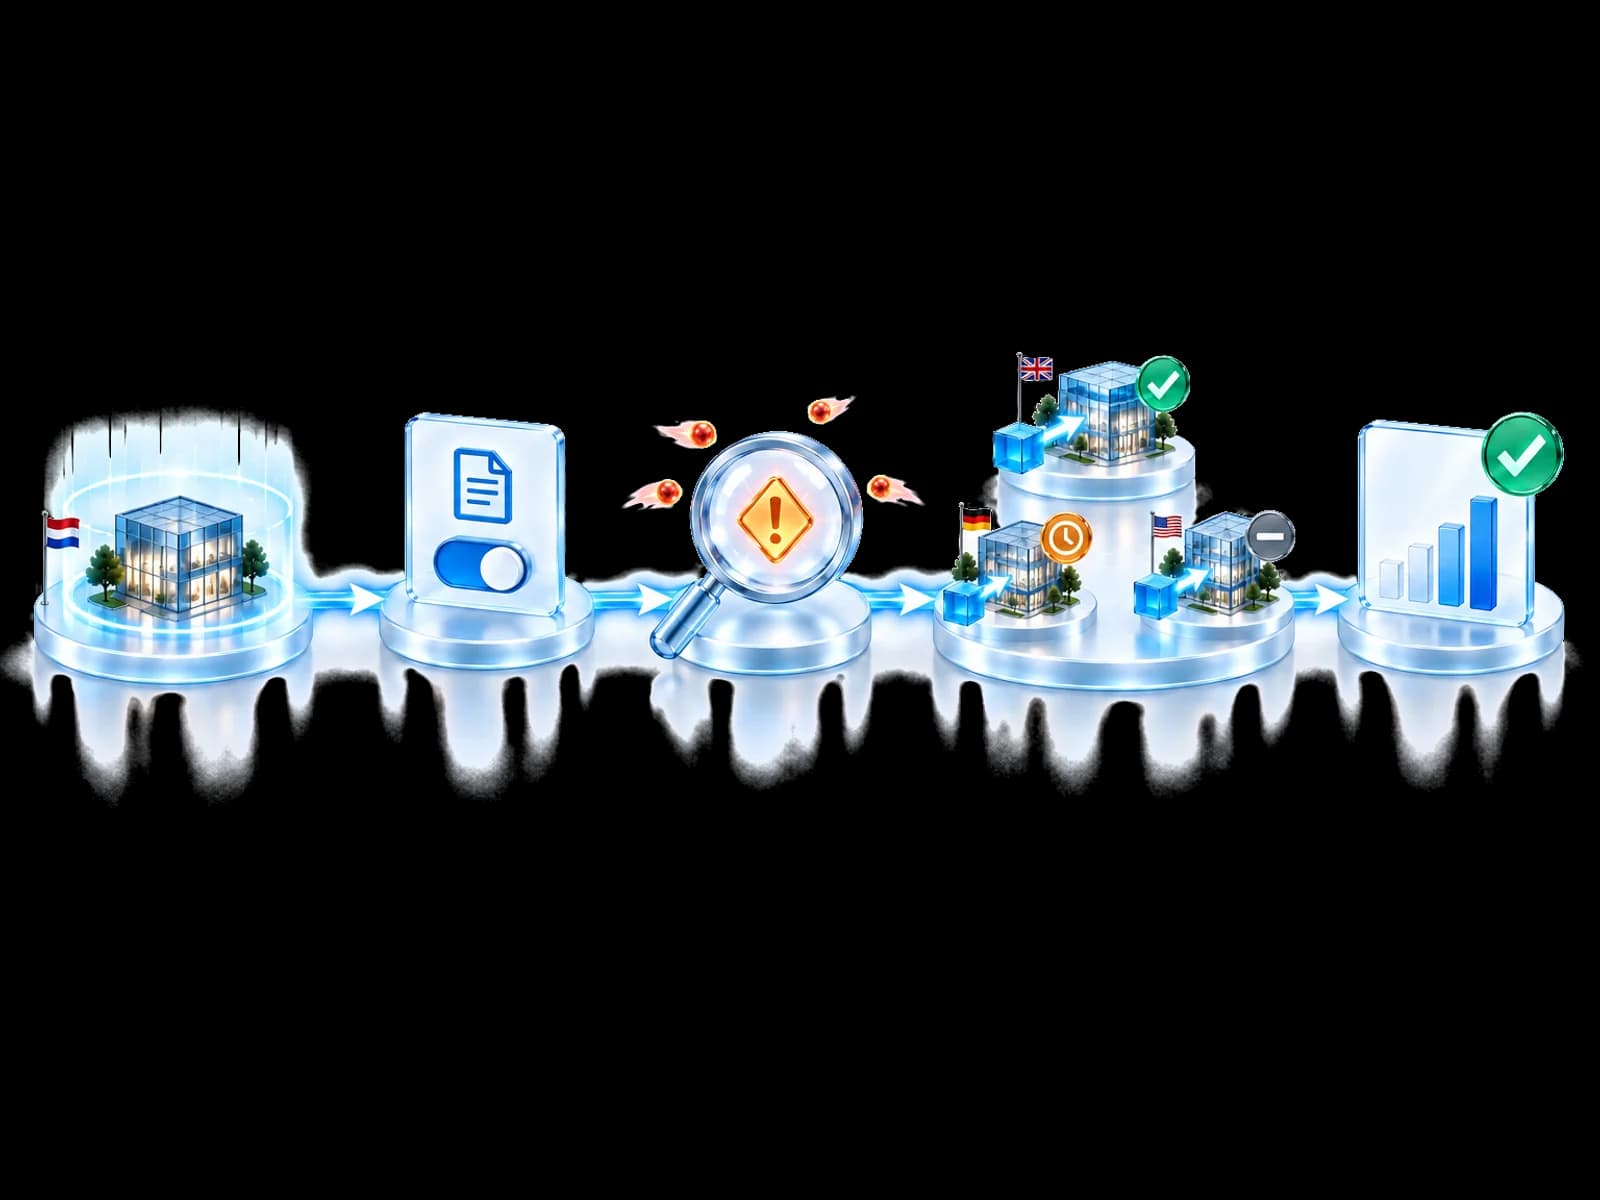
After MSP approval, connect customer tenants with Entra ID P1 or higher and Global Administrator consent.
Set policy and agree who approves which actions, per customer.
A threat reaches one customer. Your team works it once, in one place.
The validated finding reaches relevant customers under their own controls.
Report what was applied, approved or missing for each customer.
Built around Microsoft. Designed to work alongside your existing security.
Keep your existing security tools and the protection they already provide. UnifiedONE complements your investment by connecting validated threat intelligence and helping protect supported Microsoft identities, sign-ins and email. Customers using other endpoint security products can still connect eligible Microsoft tenants. No forced replacement.
Endpoint security your customers can keep
Your endpoint security keeps protecting devices as it does today.
Validated threat intelligence can inform protection for other eligible tenants.
Supported actions run through Microsoft controls in each eligible tenant. Email protection depends on the tenant's Microsoft services and licences.
Microsoft Defender for Endpoint is integrated with UnifiedONE today: where it is licensed, configured and authorised, supported device actions can run through it. Integrations with the other endpoint vendors listed are planned as part of our multi-vendor roadmap; today UnifiedONE does not act through them. IT management and security platforms such as Kaseya and ConnectWise, and managed security services such as Arctic Wolf, stay in place too.
We replace nothing. We strengthen your security alongside what you already have.
The protection outcome
Select a customer to see why the same validated finding leads to a different result.
Select a customer
Customer B allows automatic action for validated phishing domains, and the email control is connected.
Outcomes depend on relevance, local policy, permissions, supported controls and licensing.
Business value
Built for providers who own the customer relationship and the service model.
Bring a validated finding into the next eligible customer review instead of repeating the same investigation.
Validated threat intelligence can inform protection for other eligible tenants, where they have the required controls, licences and authorisation.
Once a tenant is connected, see where Microsoft licences and controls limit the available response.
Use tenant health and validated threat context to guide customer reviews and service recommendations.
Create your account and start your guided onboarding.
30-day free trial
MSPs onboard up to 15 customers with an Access Code and use the live platform on their Microsoft tenants. Not an MSP? Ask us for a code.
After 30 days, your subscription starts automatically unless you cancel.
Customer boundaries
Different MSPs, different tools, one collective defence. Privacy-safe defensive knowledge follows participation rules; customer environments and response authority stay separate.
Each customer keeps its own tenant, policies and permissions.
Decide per customer whether it receives and shares community intelligence.
Pending approvals and missing controls are never reported as protection.
Yes. Each customer keeps its own environment, policies, permissions and approvals. Sharing defensive knowledge does not give another organisation, or another customer, access to that environment.
Yes. Policy is set per customer. Pre-approved action types may run automatically only after relevance, permissions, connected controls and licences are checked. Another customer may require a named person to approve the same response.
No. Your customers keep the security tools they run today, whatever the brand. UnifiedONE adds validated intelligence and coordinates supported protection in each eligible Microsoft tenant.
The action cannot run through that control. The protection-gap view shows each connected customer where a control or licence is missing.
Plans are priced per user, per month, with flexible MSP packaging. See the pricing page, or talk to us about the model that fits your service.
Yes. MSPs can onboard up to 15 customers free for 30 days with an Access Code. We email you before the trial ends; after 30 days, your subscription starts automatically unless you cancel.
No. MSPs and MSSPs can use different security tools and vendors. UnifiedONE draws on intelligence from different sources. Today, validated intelligence is applied to connected Microsoft tenants through supported Microsoft controls.
They keep them. Microsoft Defender for Endpoint is integrated today, so where a customer runs it, UnifiedONE can also coordinate supported device actions on onboarded devices. For customers on CrowdStrike, SentinelOne, Bitdefender, ESET, Sophos or another endpoint security product, UnifiedONE can still add supported Microsoft identity and email protection in each eligible tenant, depending on its Microsoft licences, configuration, permissions and authorisation. Integrations with other endpoint vendors are planned as part of our multi-vendor roadmap.
For providers
Join the Community and activate your Access Code to try UnifiedONE with up to 15 customers, free for 30 days.
Create your account and start your guided onboarding.