NIS2 compliance
NIS2 makes security something you have to prove.
NIS2 is the EU cybersecurity directive that holds organisations and their management accountable. UnifiedONE helps you keep current evidence of your security measures and incident response, so a review starts from records instead of a scramble.
Evidence that supports your NIS2 work. Not a compliance certificate.
Create your account and start your guided onboarding.
UnifiedONE does not give legal advice or decide whether NIS2 applies to you.
- Built in Europe
- Designed for European privacy expectations
- Evidence from your live configuration
- Your team keeps the conclusions
The problem
Most organisations have the measures. Few can prove them on demand.
Evidence sits in different tools, spreadsheets and inboxes. Pulling it together for a review, or during an incident, takes time you do not have.
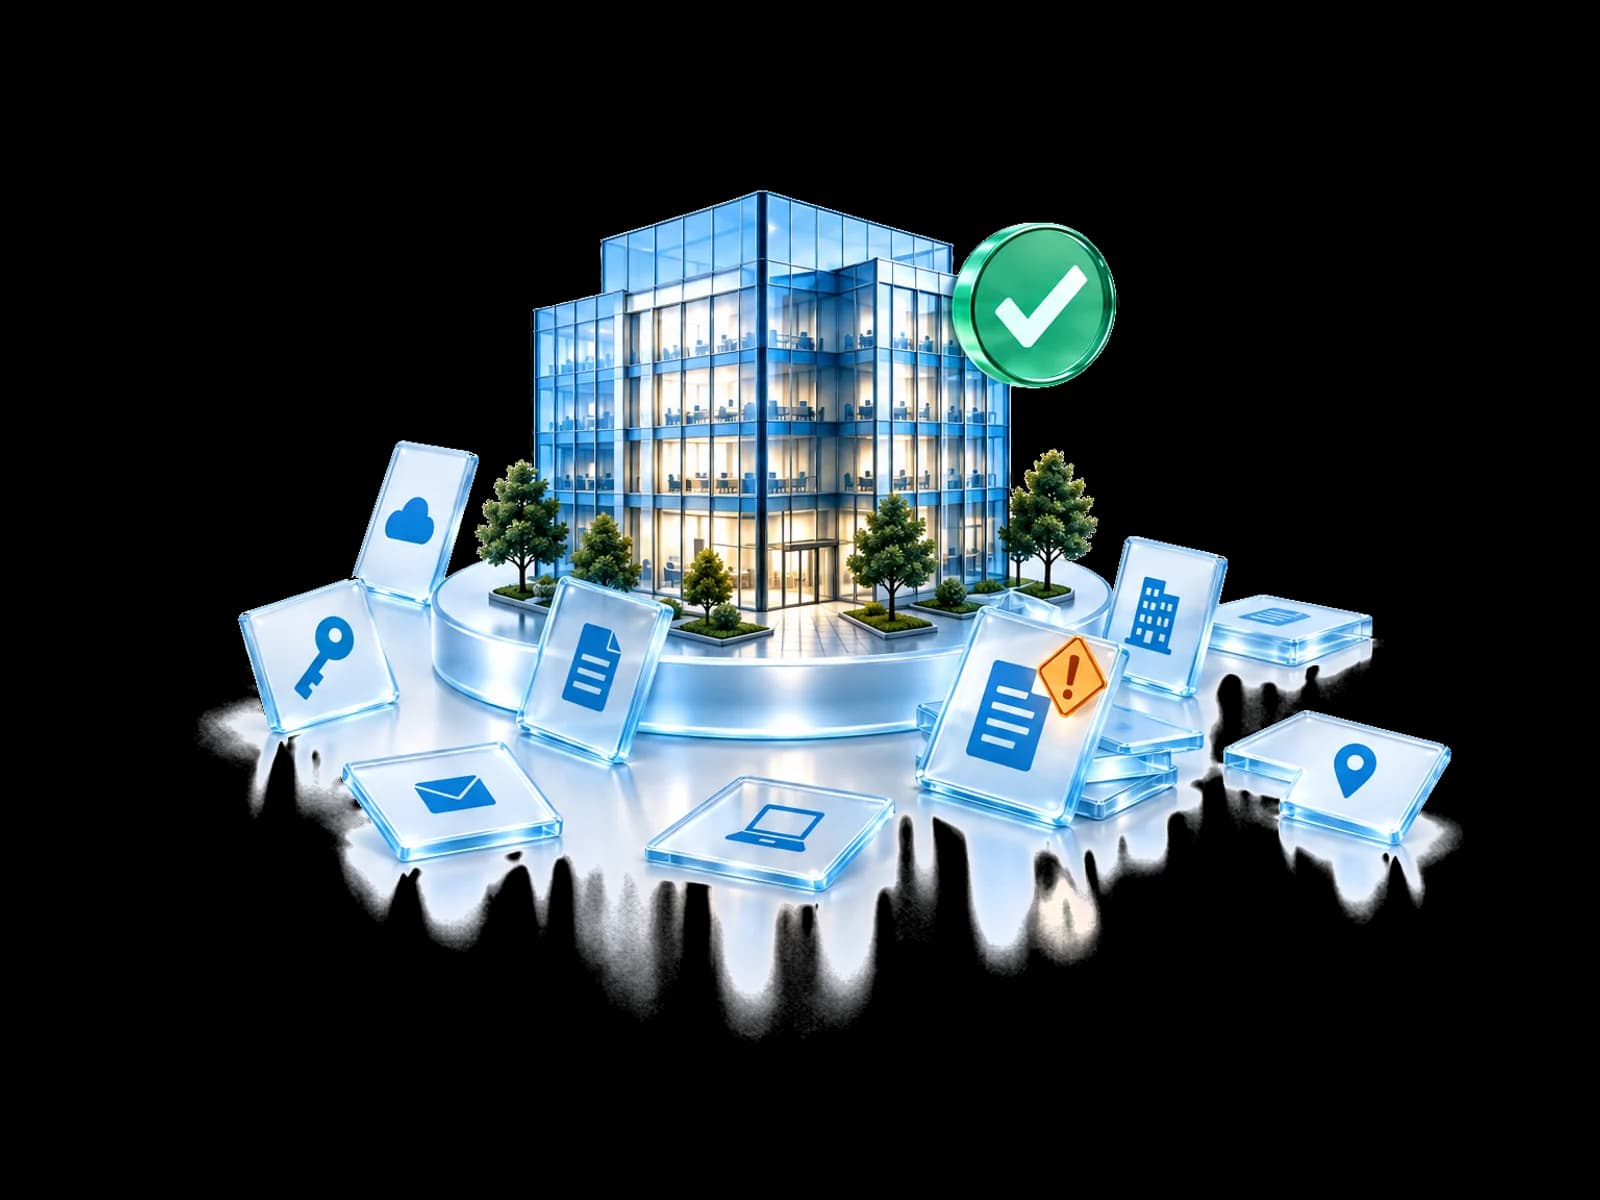
Today: Evidence is scatteredPolicies, logs and approvals live in different tools and folders.
With UnifiedONE: Security decisions and their evidence are kept together.
Today: The reporting clock is shortAn early warning is due within 24 hours of becoming aware of a significant incident.
With UnifiedONE: Incident records start from connected evidence, not a blank page.
Today: Management is accountableLeaders must approve and oversee the risk measures, and can be held liable.
With UnifiedONE: Clear, current records help management show oversight.
NIS2 in brief
What the directive asks of you.
NIS2 sets one cybersecurity baseline across the EU, with wider scope, stricter duties and personal accountability for management.
- Directive (EU) number
- 2022/2555
- Deadline for national law
- 17 Oct 2024
- Maximum fine for essential entities, whichever is higher
- €10m or 2%
From becoming aware of a significant incident
- 24 hoursEarly warning
- 72 hoursIncident notification
- 1 monthFinal report
A plain-language summary of Directive (EU) 2022/2555. National laws differ, so check your national transposition and take legal advice.
Read the detail
What is NIS2?
NIS2 is the second Network and Information Security Directive, Directive (EU) 2022/2555. It sets a common cybersecurity baseline across the European Union and replaces the original 2016 NIS Directive with wider scope, stricter requirements, and real accountability for senior management.
The intent is straightforward: raise the level of cyber resilience for the organisations that society depends on. Where the old rules covered a narrow set of operators, NIS2 pulls in whole sectors and holds each organisation to a documented standard of risk management, incident reporting, and supply chain security.
Who does NIS2 apply to?
NIS2 generally covers medium and large organisations in designated sectors, with exceptions for some smaller critical providers. A supplier may also face requirements from an in-scope customer. Exact duties depend on the national law that applies to the organisation.
The directive sorts organisations into essential entities (sectors such as energy, transport, banking, health, water, digital infrastructure, and public administration) and important entities (including postal services, waste management, chemicals, food, manufacturing, and digital providers). Both must meet the same security duties; the difference is mainly in how strictly they are supervised.
What NIS2 requires
NIS2 is built around the risk management measures in Article 21, strict incident reporting duties, and the management accountability set out in Article 20. In practice it comes down to five things you have to do and be able to prove.
- Risk management measuresAdopt technical and organisational measures across your networks and information systems: access control, MFA, encryption, patching, backups, and business continuity.
- Incident reportingReport significant incidents on a strict clock: an early warning within 24 hours, a fuller notification within 72 hours, and a final report within one month.
- Supply chain securityAssess and manage the cyber risk your suppliers and service providers carry, because an attacker who arrives through a vendor is still your incident to report.
- Management accountabilitySenior management must approve and oversee the risk measures and can be held personally liable. Cybersecurity becomes a board responsibility, not just an IT task.
- Continuous complianceKeep evidence current. Supervisors can ask at any time, so posture, policies, and incident records have to be ready on demand, not assembled after the request.
Deadlines, and what non-compliance costs
NIS2 entered into force in January 2023. Member states were required to transpose it into national law by 17 October 2024. National implementation and enforcement status vary, so check the law and authority for your country.
The penalties are meaningful. Essential entities can face fines up to €10 million or 2% of global annual turnover, whichever is higher; important entities up to €7 million or 1.4%. Beyond fines, supervisors can hold management personally accountable, which is why NIS2 has moved from an IT topic to a board one. For organisations in the financial sector, NIS2 sits alongside DORA and its own operational resilience requirements.
How it works
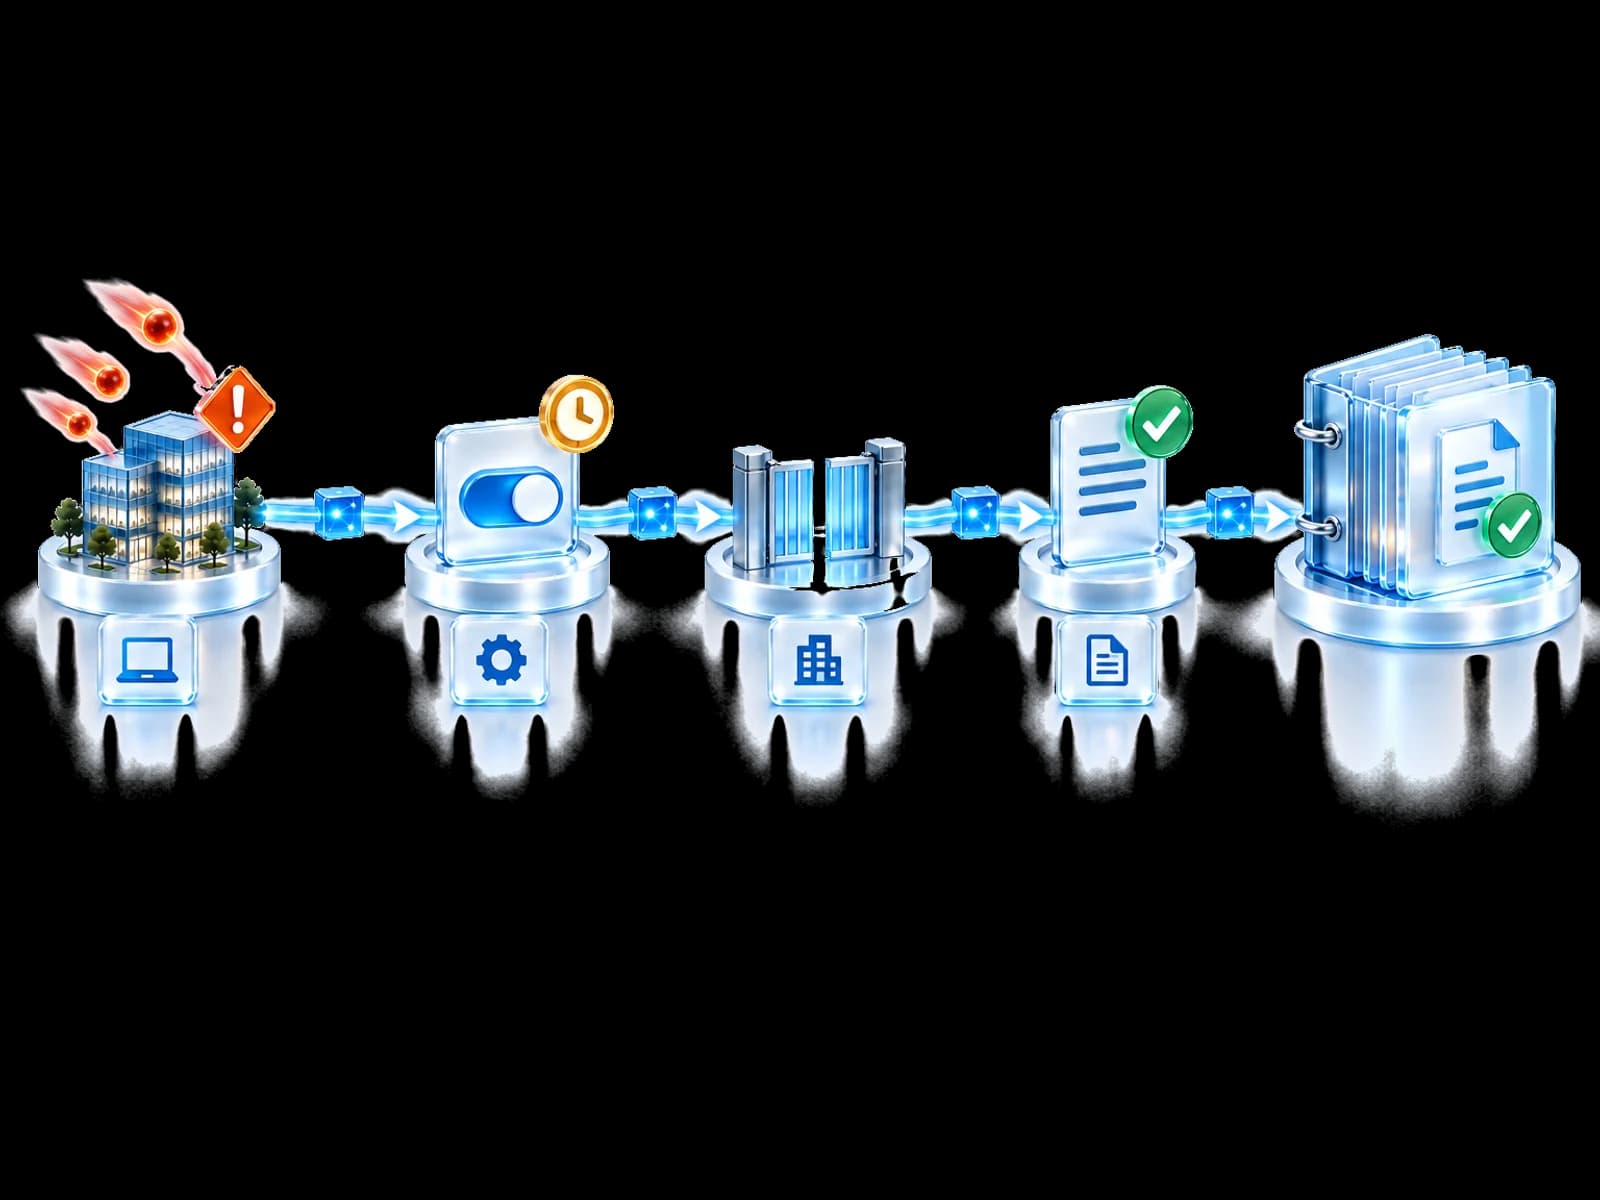
Every security decision leaves a record.
Evidence is a by-product of the work itself, not a report assembled afterwards.
- 1
Detect
Signals from connected tools and the community reveal a threat.
- 2
Assess
The finding is validated and its relevance checked.
- 3
Approve
Your policy or an authorised person decides the response.
- 4
Act
Eligible actions run through your existing controls.
- 5
Record
Evidence, rationale and outcome are kept for review.
Evidence for your review
Know what you can show and what still needs work.
Select an NIS2 area to see what UnifiedONE can help you evidence, and what stays with your team.
Select an area
Control Fabric records your configuration baseline, drift and corrections across connected environments.
This is a guide to organising evidence. It is not legal advice or a compliance assessment.
Business value
Less scramble. More confidence.
Evidence that stays current supports every review, audit and board conversation.
Review-ready records
Decisions, approvals and outcomes are kept together as the work happens.
One source for several frameworks
The same evidence can support NIS2, DORA and GDPR discussions.
Board visibility
Board-Ready Evidence turns operational records into clear reporting.
Built for European expectations
Built in Europe and designed around European privacy expectations.
Create your account and start your guided onboarding.
Clear boundaries
Evidence supports compliance. It does not certify it.
NIS2 duties depend on your sector, size and national law. Your legal and security teams stay responsible for the conclusions.
See board-ready evidenceNo legal advice
UnifiedONE does not decide whether NIS2 applies to you or interpret national law.
No compliance badge
Records support your review. They do not establish compliance by themselves.
No reporting on your behalf
Notifications to authorities remain your organisation's decision and action.
What is NIS2?
NIS2 is Directive (EU) 2022/2555, the European Union's updated cybersecurity law. It replaces the 2016 NIS Directive with wider sector coverage, stricter risk management and incident reporting duties, and direct accountability for senior management.
Who does NIS2 apply to?
It generally covers medium and large organisations in designated sectors, with exceptions for some smaller critical providers. Suppliers may face customer requirements. Check the applicable national law for scope and duties.
Does NIS2 apply to my company?
Sector, size, role and national law all matter. Supplying an in-scope entity may create contractual requirements, but it does not by itself establish that the directive applies directly to you. Check national law and seek legal advice.
When did NIS2 take effect?
NIS2 entered into force in January 2023, and member states were required to transpose it by 17 October 2024. Check your country's implementation and enforcement status for the applicable duties.
What are the penalties for non-compliance?
Essential entities can be fined up to €10 million or 2% of global annual turnover, whichever is higher; important entities up to €7 million or 1.4%. Management can also be held personally liable.
How is NIS2 different from the original NIS Directive?
NIS2 widens the sectors and organisations in scope, standardises security and reporting requirements across the EU, adds supply chain and management accountability duties, and raises penalties. It closes the gaps and inconsistencies the first directive left behind.
Next step
Start your NIS2 review from evidence.
Join the Community to connect your environment through guided onboarding, or talk to us about your review.
Create your account and start your guided onboarding.