
Alert by alertGuesswork
The response is a guess.
Without connected evidence, the choice is between doing too little and doing too much.
Endpoint & Device Protection
UnifiedONE connects device, identity and email evidence, then coordinates a supported containment step, up to isolating the device, through Microsoft Defender for Endpoint on onboarded devices. Another endpoint product keeps protecting its devices, and integrations with other endpoint vendors are planned.
Contain the threat. Keep people working.Create your account and start your guided onboarding.
The problem
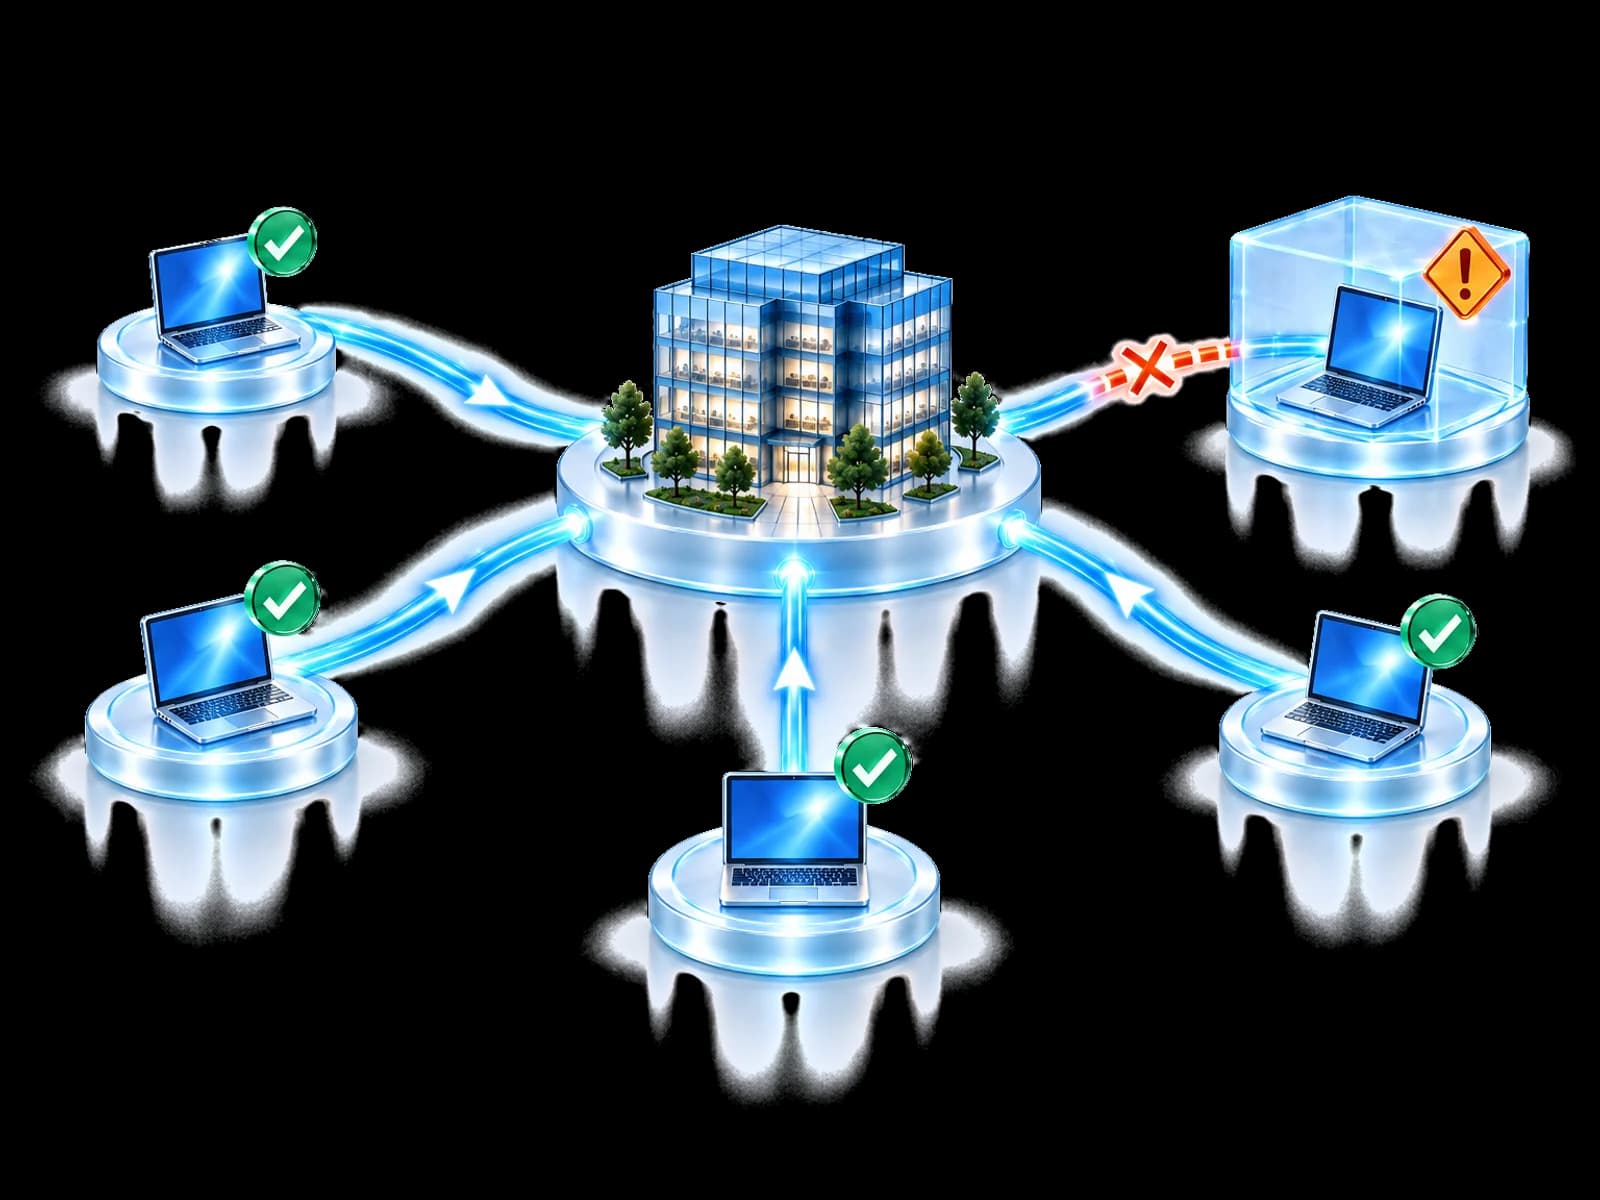
One endpoint alert rarely tells the whole story. Teams either wait and risk the spread, or cut the device off completely and stop the person working.
Without connected evidence, the choice is between doing too little and doing too much.
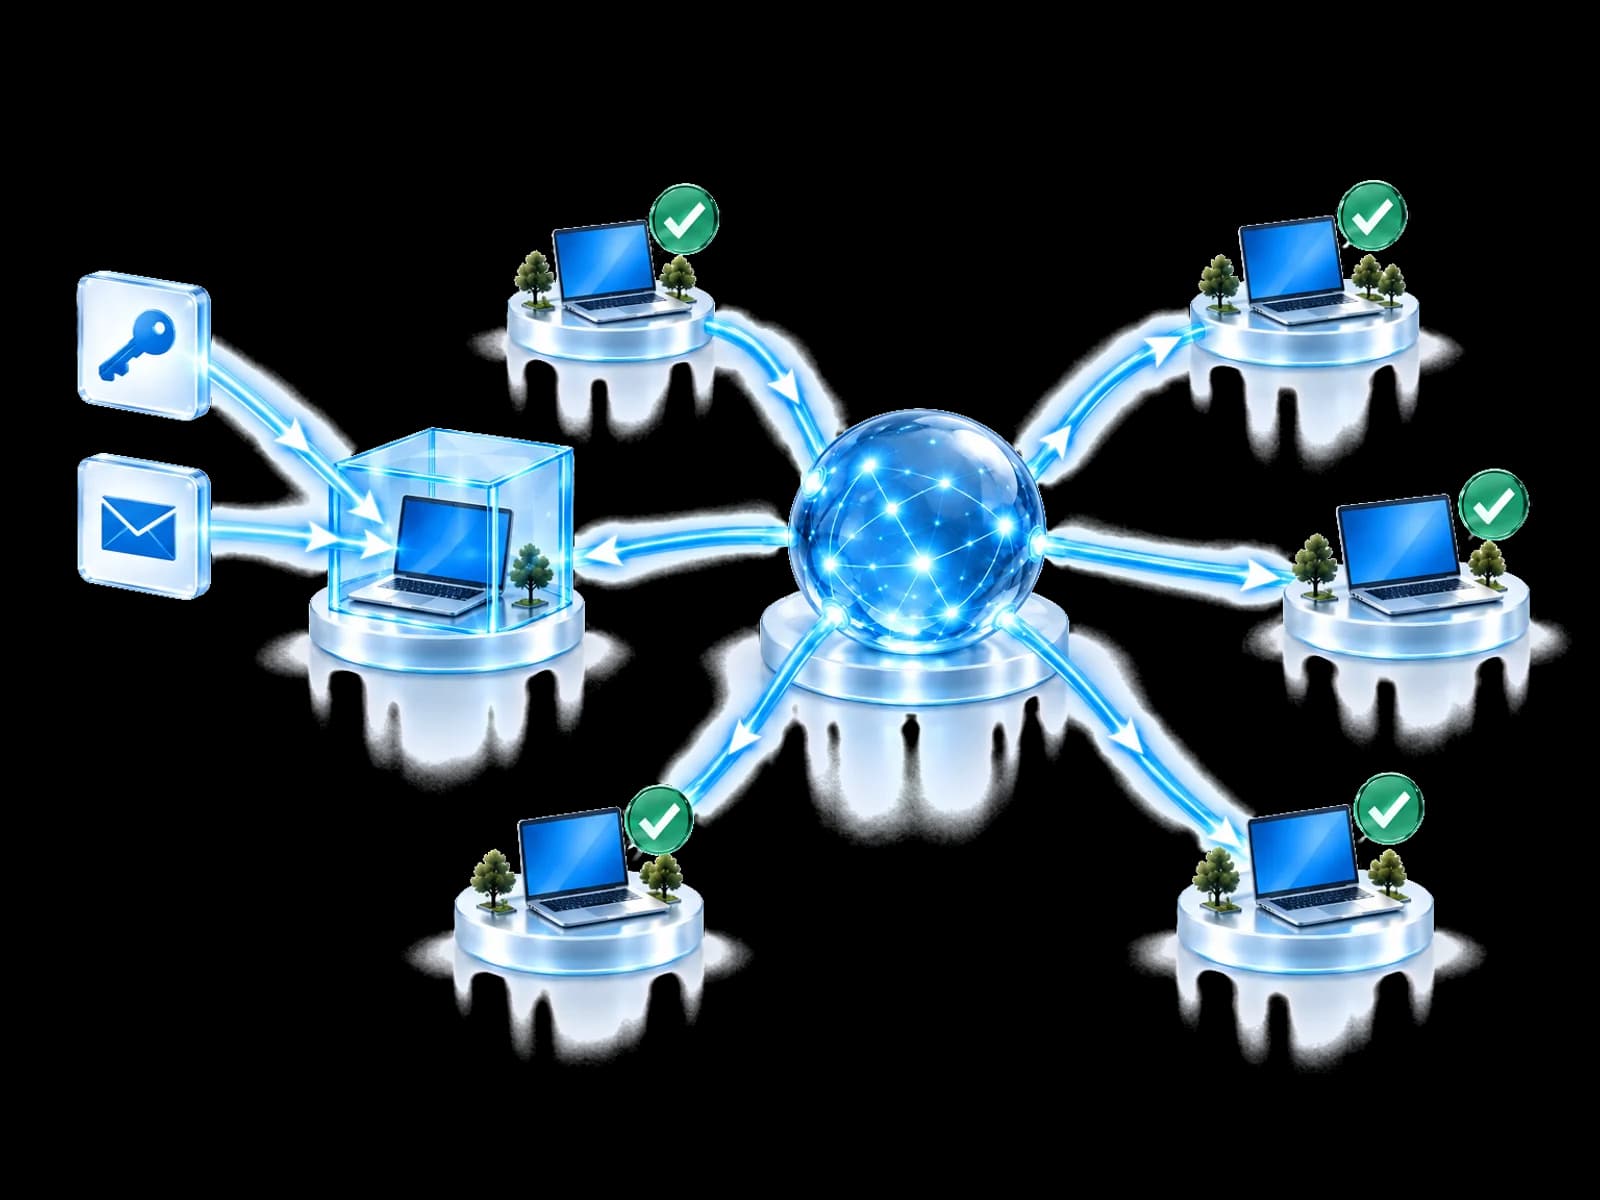
UnifiedONE weighs the combined evidence and proposes the containment level your policy allows, then checks what Microsoft Defender for Endpoint reports back.
Containment level
The chosen level must fit the evidence, local authority and available endpoint control.
Result: a person can choose the next approved step.
Read the outcome
Provider read-back makes partial, delayed and unverified outcomes visible while keeping device data private.
A provider accepting a request does not prove the device reached the intended state.
Defensive knowledge can travel. Device records do not.Validated attacker indicators can help protection without sharing a customer device or investigation.
Endpoint actions remain conditional on local policy, permissions, licensing, device reachability and documented provider capability.
Built for your team
Stop an infected laptop quickly without an in-house security team.
Apply consistent containment across customer devices, with each customer's approval.
Contain threats on critical devices without disrupting whole departments.
Choose containment with device, identity and email evidence side by side.
Questions people ask
UnifiedONE does not scan files or memory, detect malware or install an agent on the device. Microsoft Defender for Endpoint is integrated with UnifiedONE today: where it is in place, Endpoint & Device Protection correlates its findings with identity, email and community evidence, decides what level of containment the evidence justifies and coordinates that action through Defender for Endpoint. With another endpoint product, keep it; integrations with other endpoint vendors are planned as part of our multi-vendor roadmap.
Containment is a ladder, not a switch. Collecting evidence costs the user nothing. Blocking a payload stops one program. Restricting the signed-in identity costs a sign-in. Cutting the device off the internet stops mail and web. Full isolation stops the machine. UnifiedONE is designed to choose the lowest rung that holds the attack and to record why the rungs above it were not used, because somebody has to pay for those.
No. Keep your endpoint product, whatever the brand. Microsoft Defender for Endpoint is integrated today, so device actions run through it on onboarded devices where it is in place. Integrations with other endpoint vendors are planned as part of our multi-vendor roadmap; today UnifiedONE does not send actions to them. Where a control or a licence is missing, the limitation is shown rather than hidden behind a successful-looking result.
Only if you decide it can. Autonomy is set per action. In Observe nothing changes on the device. In Assist a named person approves. In Act only the rungs you approved may run on their own, and devices can be marked so the disruptive rungs always need a person first.
It is reported as waiting, not as contained. A command that cannot land has not landed. Where the evidence allows it the containment can be sized differently instead, since restricting the identity's sessions does not need the laptop to be awake.
No. Wipe, reimage and factory reset are not part of this, and UnifiedONE does not read the contents of customer files. Containment is about removing the attacker's access, not about erasing the machine or inspecting what is on it.
No. What can travel is attacker knowledge: file hashes, malicious addresses, domains and URLs, campaign identifiers, and confidence and expiry metadata. Device names, device telemetry, file contents, usernames, customer and tenant names and investigation evidence are not shared between participants.
That is the case it is designed for. One containment workspace across every customer, with tenant isolation and customer authority preserved. An MSP can see which tenants can actually contain a device, which need an approval first, and which lack the capability or the licence, without opening a console per customer.
Start here
See how UnifiedONE is designed to turn one endpoint detection into a correlated decision, a containment sized to the evidence, and a result that was read back rather than assumed.
Create your account and start your guided onboarding.