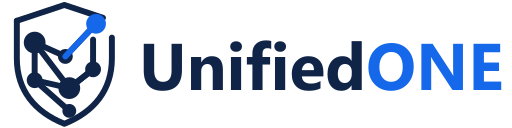
Tenant by tenantRepeated work
The same work, tenant after tenant.
Repeated investigation can delay the next local decision.
Cross-Tenant Protection
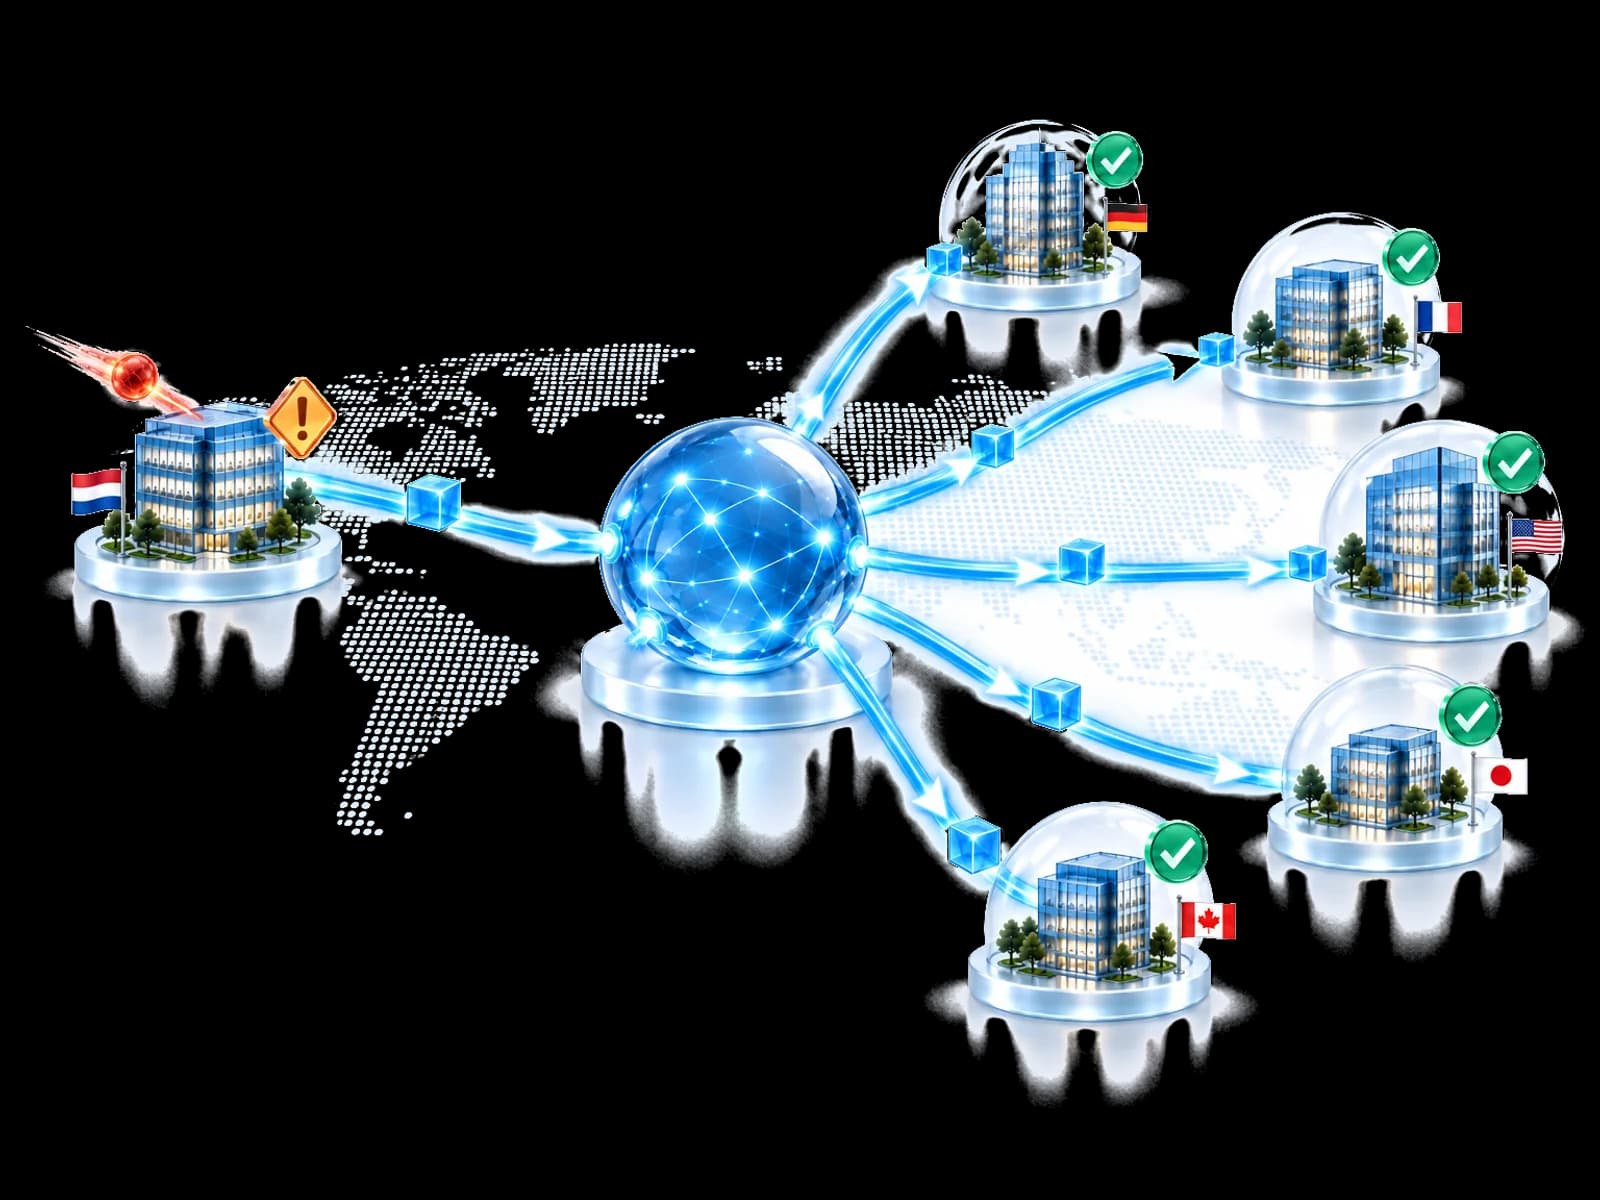
When a threat is validated in one environment, UnifiedONE can make the defensive lesson available to other participating environments. Each checks relevance, policy, permissions, connected controls and licences before a local response. The private investigation stays at its source.
One finding. More teams ready.Create your account and start your guided onboarding.
The problem
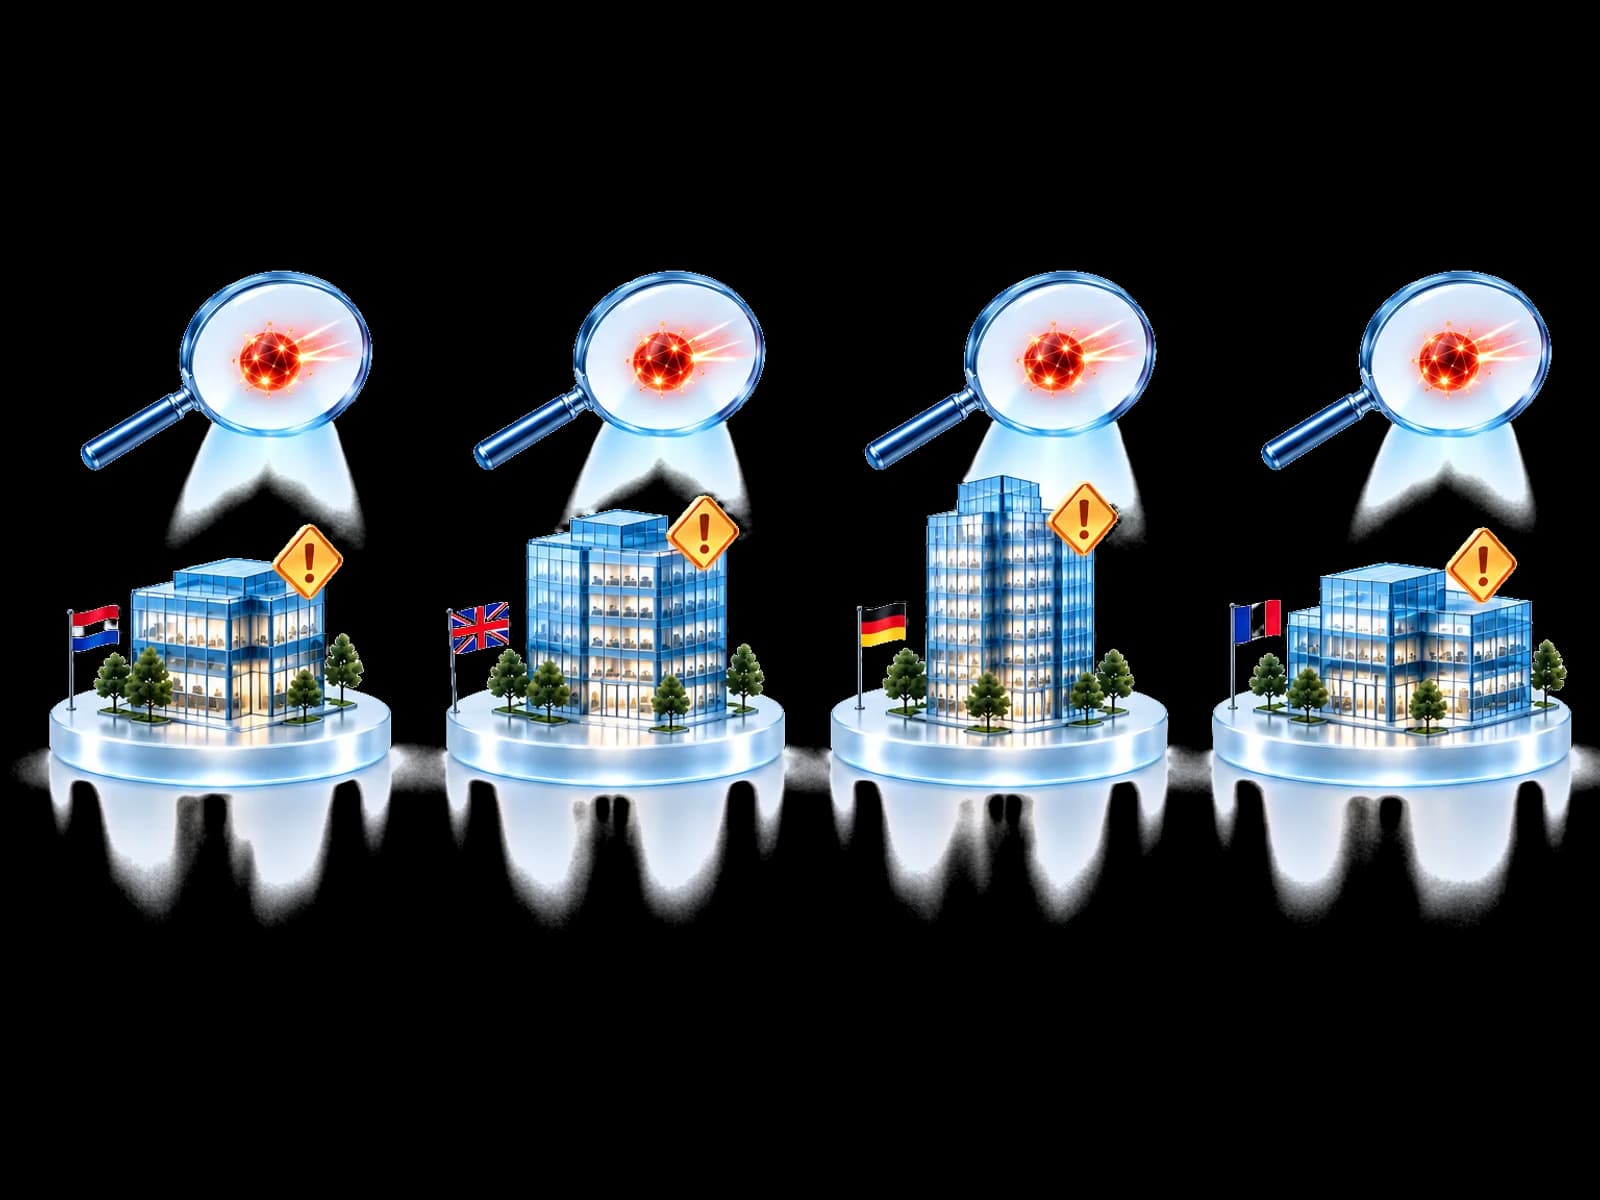
An MSP or a group may see the same attack across many environments. Without a governed way to reuse the defensive lesson, teams can repeat investigation before deciding what applies locally.
Repeated investigation can delay the next local decision.
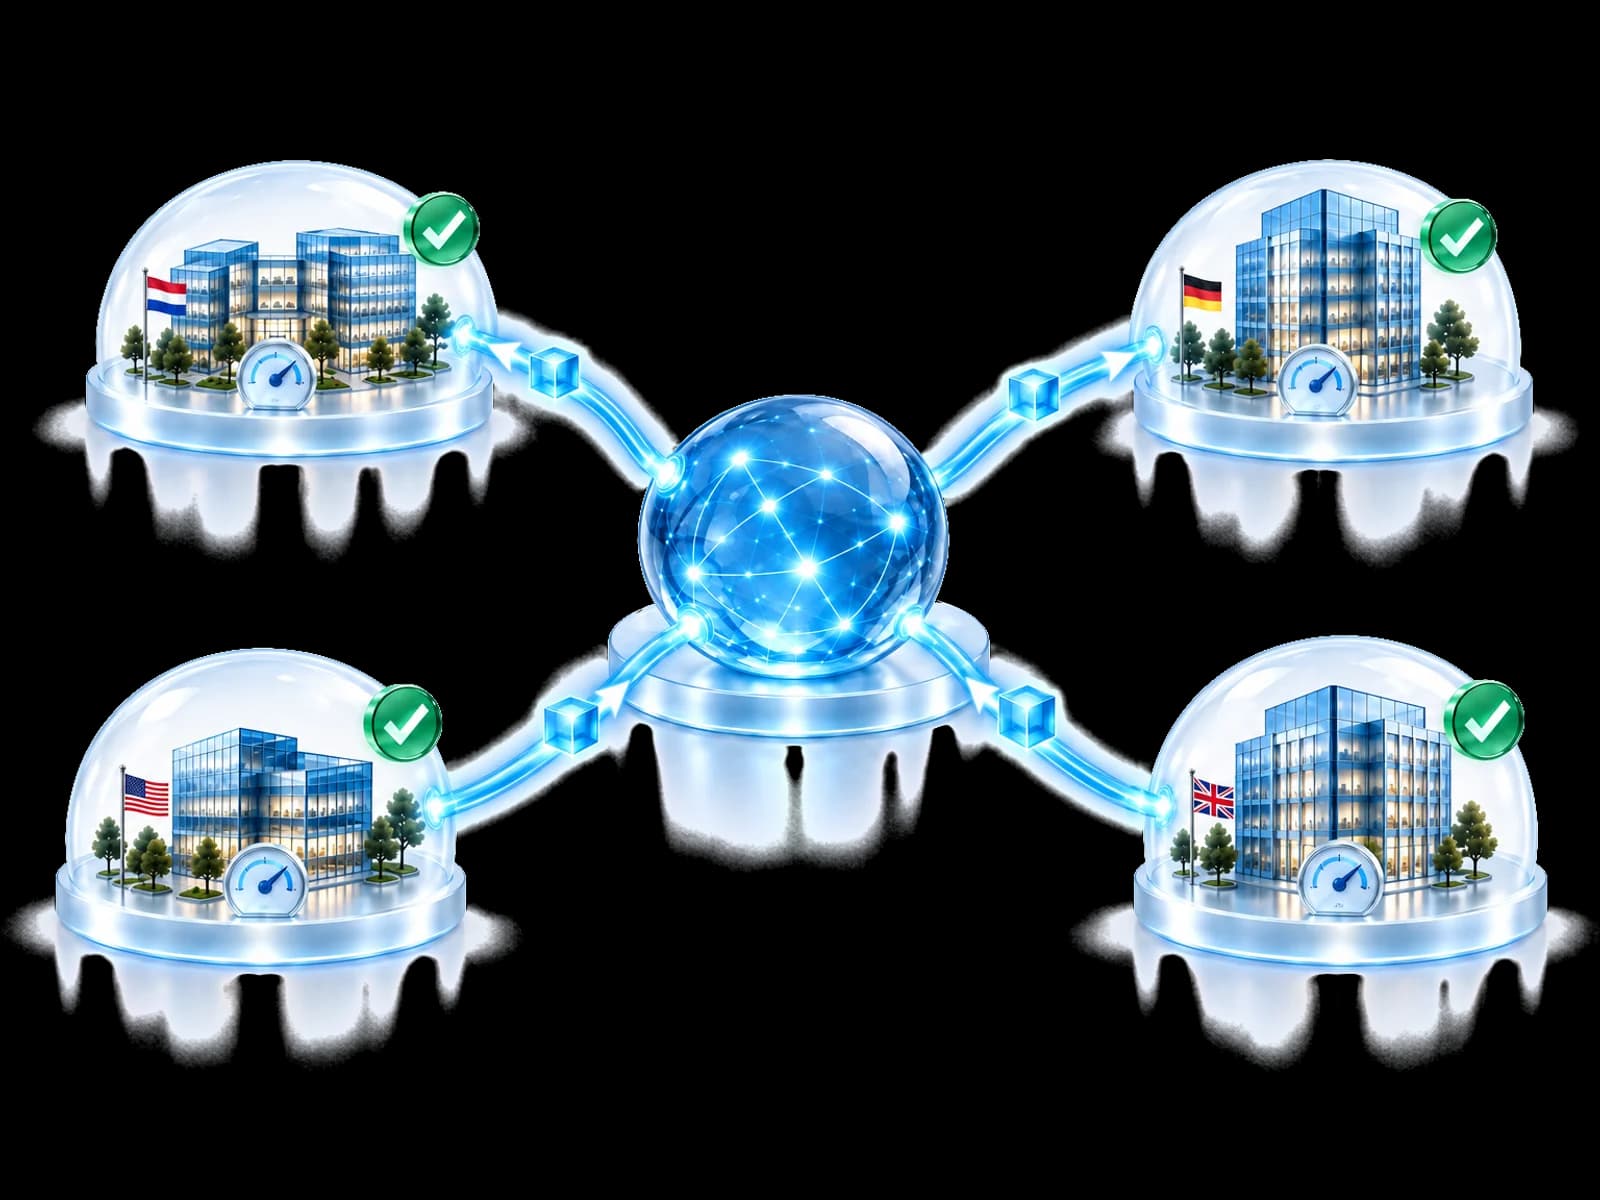
The lesson crosses the boundary; control does not. Each tenant's policy, permissions and licences decide its response.
How it works
Choose how the lesson arrives, then compare three independent recipient decisions. Participation never means the same action runs everywhere.
Illustrative recipients and outcomes. No customer records or live activity.
Cross-Tenant Protection evaluates a defensive lesson for each participating environment. It does not provide tenant access or transfer the case that produced the lesson.
Built for your team
Use relevant validated findings from participating environments through the controls you already have.
Reuse an investigation across eligible customers while each keeps its own authority.
Help business units act on relevant findings without flattening local policy.
Carry a confirmed finding into the next eligible response.
Questions
Privacy-safe defensive knowledge can travel: attacker indicators, validation, confidence, expiry and attack patterns. Customer and tenant identities, users, messages, files, raw records, investigation notes and tenant access remain local.
No. Observe changes nothing. Assist prepares an eligible response for a named approver. Act applies only to pre-approved action types and still depends on relevance, local policy, connected controls, permissions and licensing.
The lesson can remain visible, but the response cannot be presented as successful protection. The missing capability or licence stays named for that recipient environment.
No. Provider acceptance is different from an observed protection state. Continuous Protection Assurance and the Assurance Center are planned capabilities delivered in phases.
No. Different security ecosystems can contribute intelligence to one common operational layer. Today, protection can be applied to connected Microsoft tenants through the Microsoft security tools they already use.
Start your onboarding
Join the community and keep every recipient's policy, approval and controls independent.
Create your account and start your guided onboarding.